Description
Site broken after a plugin update? Seeing “There has been a critical error on this website”, a white screen of death, a checkout or contact form that silently stopped working, or a 500 error? Something in your plugin list did it, and Tracedown finds out which one, in minutes, without deactivating anything and without touching what your visitors see.
You cannot get stuck. Tracedown never writes the active_plugins option. Not once, on any code path. It filters the active plugin list in memory, for one signed-in administrator, for the length of one expiring session. Because nothing is written, restoring is not an operation Tracedown has to perform correctly. There is nothing to undo. Doing nothing restores the site when the session expires. Deleting one file restores it instantly.
That is a checkable claim, not a slogan. Search this plugin for a write to the active_plugins option, or for a call to core’s plugin activation and deactivation helpers, and you will not find one. The build fails automatically if anyone ever adds one.
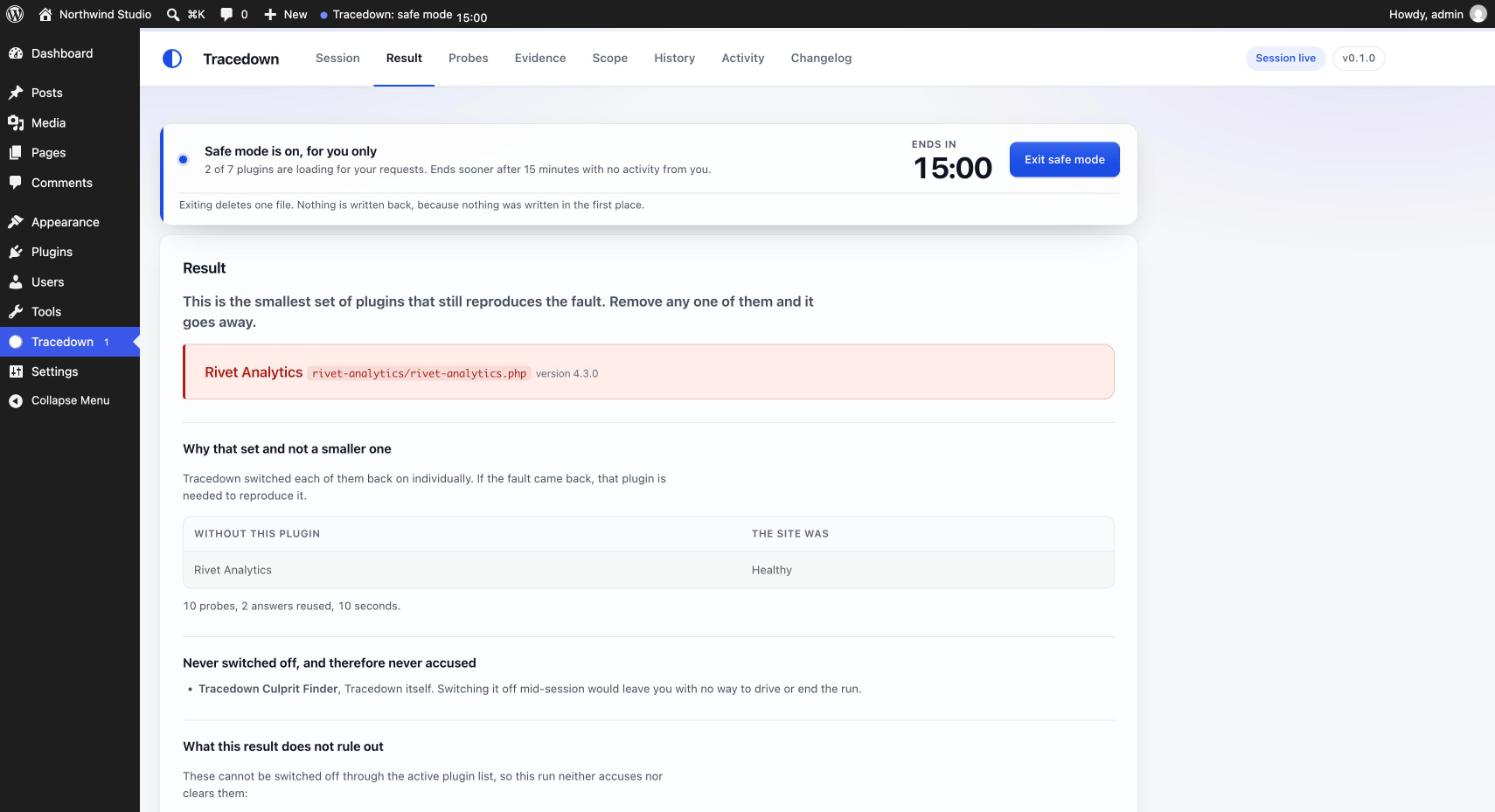
And it names the culprit. Tracedown does not hand you a list of 86 checkboxes to toggle one at a time. It runs a deterministic delta-debugging search (ddmin) over the plugins that were active when the session started and returns a minimal failing set, which stays correct when two plugins only break the site together, the case a naive one-at-a-time or split-in-half search reports as “everything looks fine”.
How the safety works
- Four independent ways out, all of them a delete or a no-op, never a repair.
- Add
define( 'TRACEDOWN_DISABLE', true );towp-config.php. It is the first thing the safe-mode file checks. - Delete
wp-content/mu-plugins/tracedown-safe-mode.phpover FTP, SFTP or your file manager. - Run
wp tracedown abort. The command is registered from the safe-mode file itself, so it works even while the plugin is filtered out. - Wait. Sessions expire on their own: 30 minutes by default, 15 minutes idle, and a hard one-hour ceiling that is written into the file rather than the database, so tampering with a database row cannot extend it.
- Add
- Visitors are not affected. The session is bound to one signed-in administrator through an HMAC-signed, HttpOnly, SameSite=Strict cookie. It is never bound to an IP address, so a mobile network, a VPN or a CDN edge change cannot silently drop you out of safe mode and give you a false “this looks clean” reading. Tracedown’s own loopback checks run logged out and carry no WordPress login cookies; each one proves itself with a single random key that expires within a minute.
- Write attempts are blocked and logged. While a session is live, Tracedown strips plugin-management capabilities from the session user and vetoes any attempt to write the active plugin list, from any source, at the last possible moment. If something tries, you are told what tried.
- It refuses rather than half-installing. If the mu-plugins directory is not writable, file modifications are disabled, the site is multisite, a
.maintenancefile is present, another must-use plugin already filters the same list, or a test write does not read back from the database, Tracedown declines to start and tells you exactly which of those it was. - It removes itself when it should. If the Tracedown plugin folder disappears (deleted over SFTP mid-session, for instance), the safe-mode file deletes itself on the next request instead of stranding an orphan. It also deletes itself after two consecutive fatal errors attributable to its own code.
What it does not do
Tracedown states its limits rather than returning a confident wrong answer.
- It cannot test must-use plugins, drop-ins such as
object-cache.phporadvanced-cache.php,wp-config.php, your theme beyond a single default-theme comparison, WordPress core, or your host’s configuration. Those are reported as untested scope. - Plugins you pin cannot be identified as the culprit, and the report says so by name. Security, firewall, two-factor, login and SSL plugins are pinned by default.
- Multisite is refused outright in this version.
Prior art
Tracedown is an original, clean-room implementation, but it is not the first plugin to work this way and it does not pretend to be. Health Check & Troubleshooting established the mu-plugin-filters-active_plugins approach that every tool in this category, including this one, depends on. Plugin Detective popularised searching for the conflict rather than making the user toggle plugins by hand. Both are GPL, both are worth your respect, and Tracedown differs from them in architecture rather than in ambition: no write to active_plugins, expiry evaluated on read, and a deterministic minimal-set search.
What Tracedown writes to your site
Two files, both only while a session is running, both removed when it ends:
wp-content/mu-plugins/tracedown-safe-mode.php(default location): the must-use plugin that hides plugins from your own requests. It is a fixed file bundled with the plugin, copied byte for byte. Nothing you type ever reaches its contents. Deleting it ends the session immediately and returns the site to normal.wp-content/uploads/tracedown/snapshot-<site id>-<random>.json(default location): a plain JSON list of the plugins that were active when the session began. It exists sowp tracedown restorecan read the original list even if the database record and the plugin itself are gone. It is data, never code. Its name carries a random part so it cannot be guessed, and the folder also carries an.htaccessdeny rule and an emptyindex.php.
A small number of tracedown_* rows are stored in the options table. Everything above is removed on uninstall.
Tracedown never writes the active_plugins option.
Screenshots
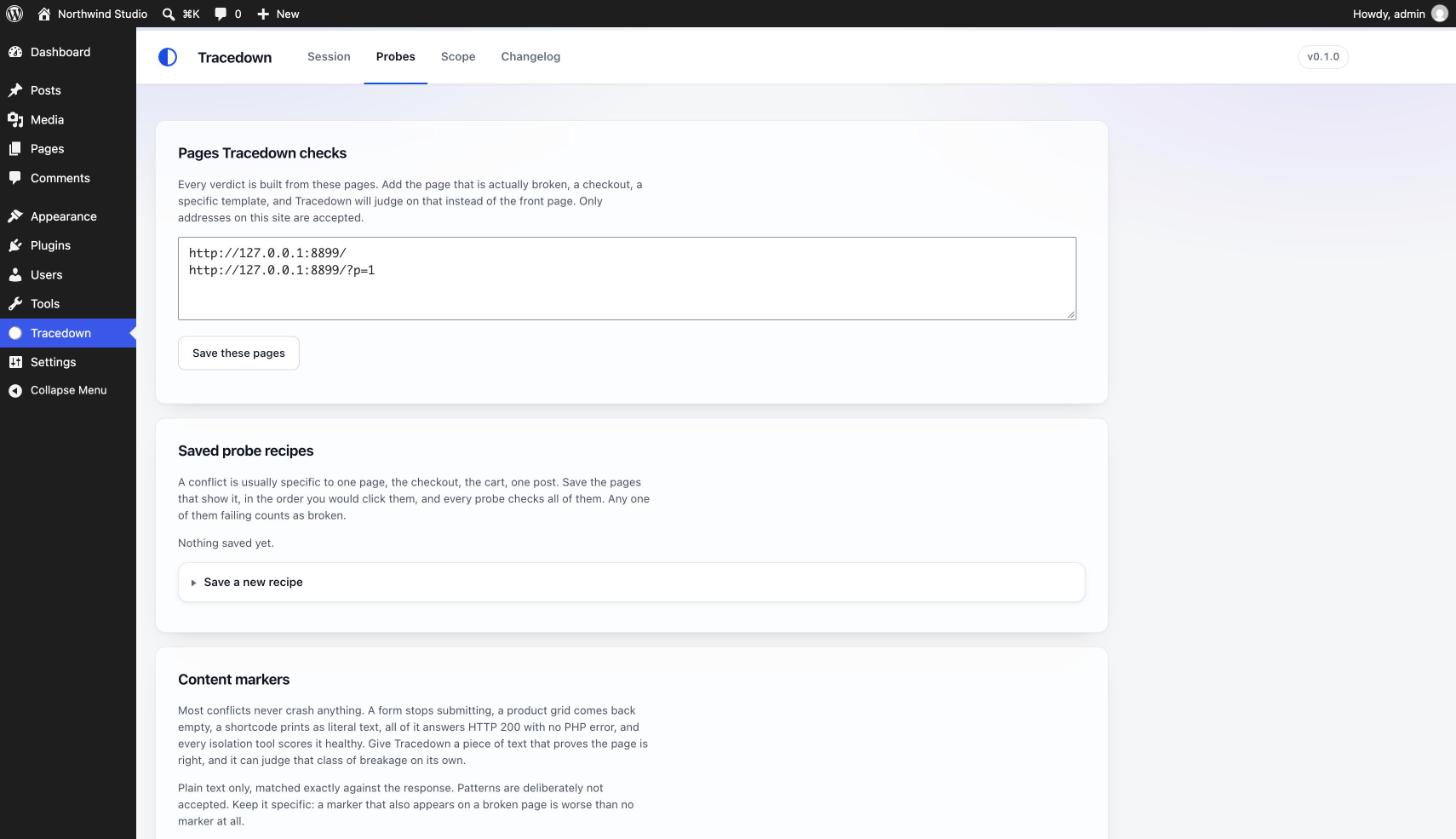
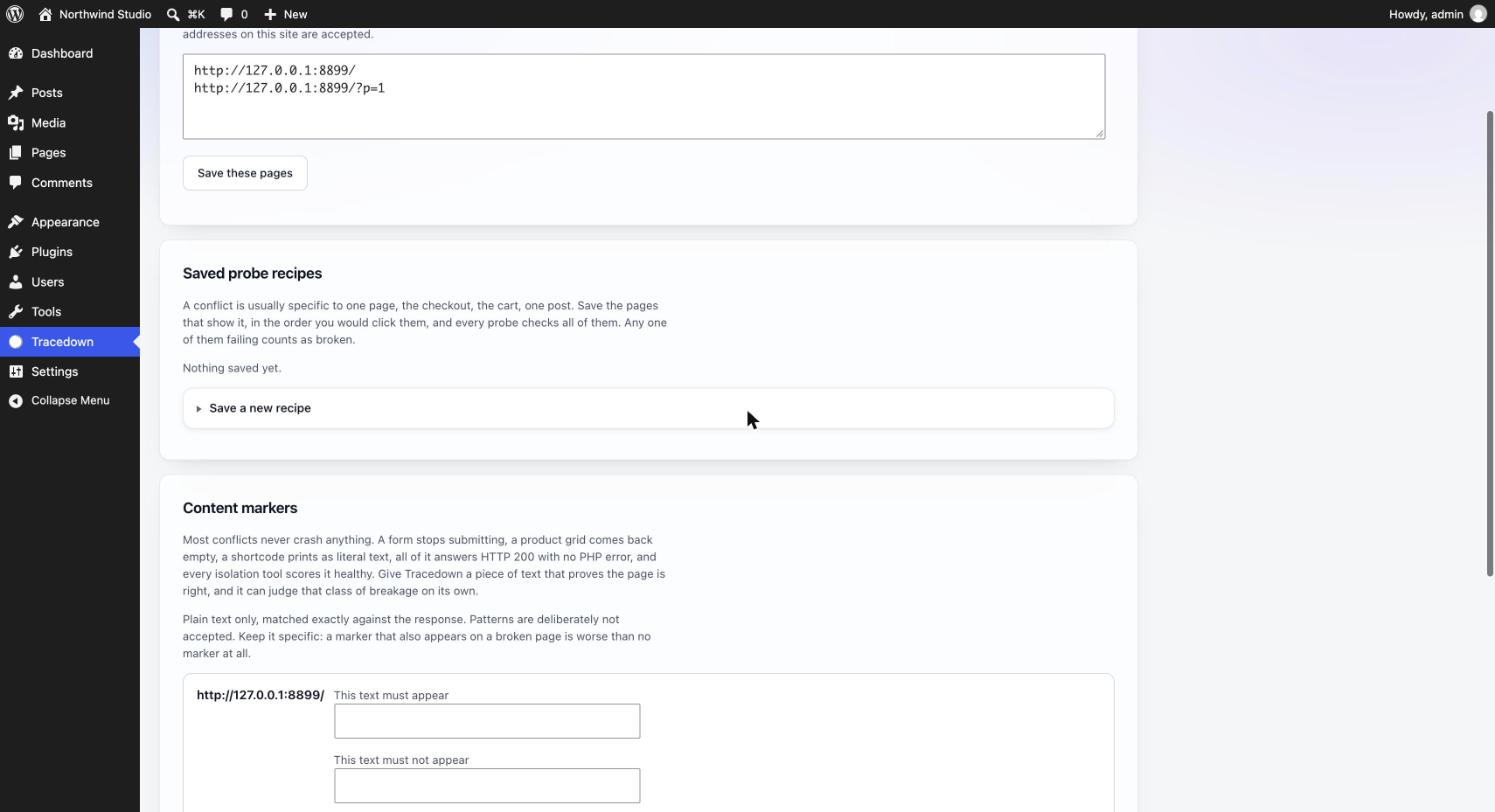
Installation
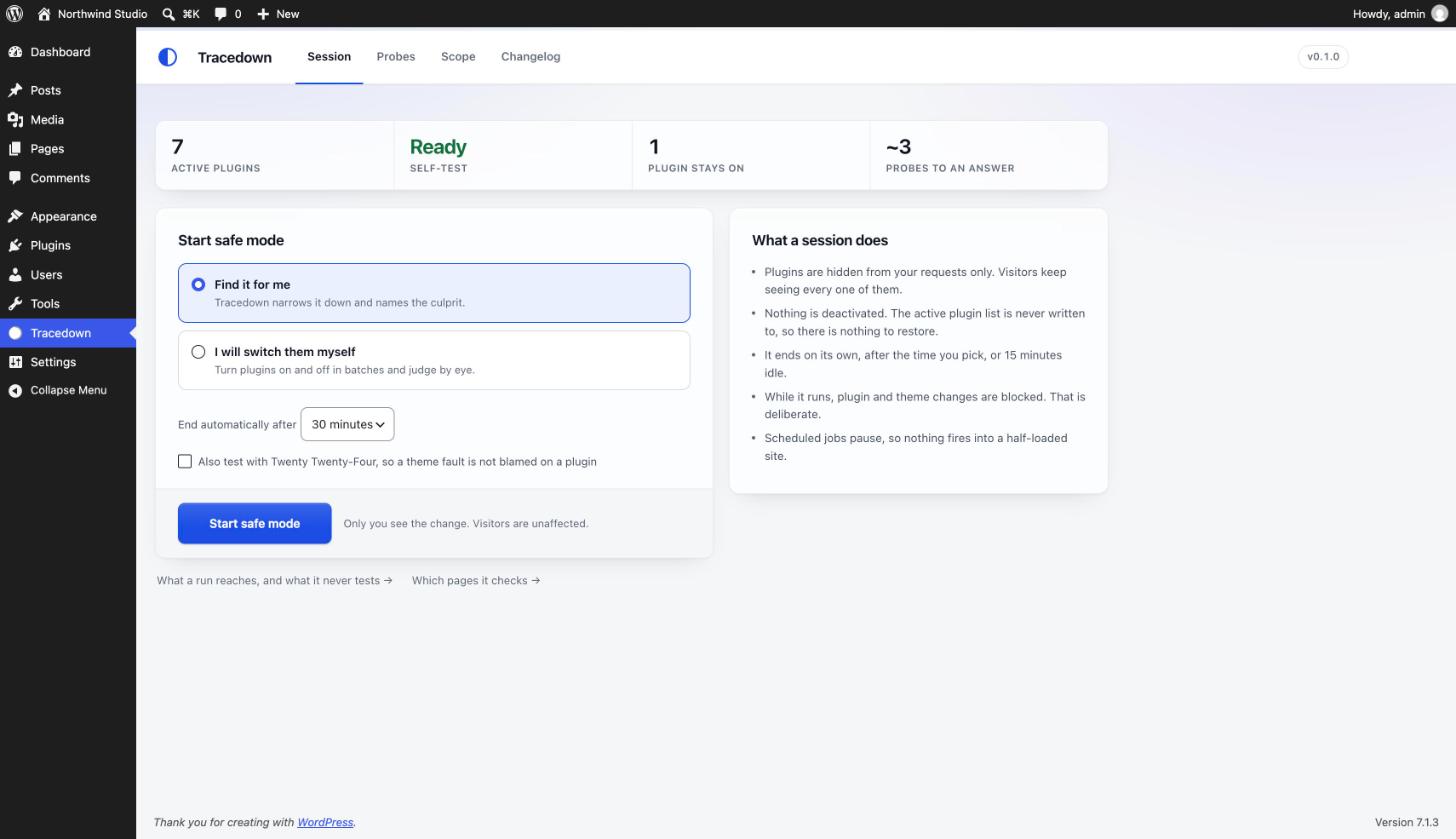
- Install and activate Tracedown like any other plugin.
- Go to Tracedown in the admin menu.
- Read the preflight result. If anything is refused, fix that first. Tracedown will not start a partial session.
- Start a session. Tracedown writes one file to
wp-content/mu-plugins/and verifies the site still responds before handing control back to you. - Isolate the conflict, copy the report, then exit. Or close the tab: the session expires on its own.
FAQ
-
My site says “There has been a critical error on this website”. Can Tracedown find which plugin caused it?
-
Yes, as long as you can still reach wp-admin. Start a session, choose “Find it for me”, and Tracedown probes your front page with different subsets of plugins loaded until it has the smallest set that still reproduces the error. A PHP fatal error, a 500, a white screen and a blank page all count as broken. If the error is also on the admin side and you cannot log in, see the next question.
-
Nothing loads, not even the login page. What now?
-
Tracedown needs wp-admin to run. If WordPress cannot start at all, rename the plugins folder over SFTP or your host’s file manager to get back in, then let Tracedown name the culprit so you only have to remove one plugin instead of guessing.
-
My site broke right after a plugin or WordPress update. How do I find which plugin did it?
-
Run a session. Tracedown tests the plugins that are active right now and returns the minimal set that reproduces the fault, so a plugin that only breaks in combination with another one is still caught. The report lists the plugin name, file and version so you can roll it back or report the bug.
-
How is this different from deactivating plugins one by one?
-
Three ways. It is faster: a deterministic halving search needs a handful of probes instead of one per plugin. It is safer: nothing is ever written to the active plugin list, so there is no “I deactivated everything and now I cannot remember what was on” moment. And it is correct for pairs: two plugins that only break together are found, where a one-at-a-time check reports every single plugin as fine.
-
How is this different from the Health Check troubleshooting mode?
-
Same family of idea, different architecture. Both use a must-use plugin to filter the plugin list for one administrator. Tracedown additionally never writes the
active_pluginsoption on any code path, so there is no restore step that can fail and leave plugins deactivated. It also runs the search for you and names a minimal set instead of leaving the toggling to you. -
Will my visitors see the site with plugins disabled?
-
No. The filter only applies to requests carrying your signed session cookie. Tracedown also marks its own responses as uncacheable so a page cache or CDN cannot store a safe-mode response and serve it to someone else. There is a button in the session bar that opens a logged-out preview so you can see this for yourself.
-
What happens if I close the tab and forget about it?
-
The session ends by itself. Expiry is evaluated every time the safe-mode file loads, so it needs no cron job, no scheduled task, no traffic and no action from you. Nothing was written to the database, so when the session ends the site is exactly as it was.
-
What happens if my site was already down when I started?
-
If WordPress cannot start at all, no plugin can help you, including this one. Add
define( 'TRACEDOWN_DISABLE', true );towp-config.phpor deletewp-content/mu-plugins/tracedown-safe-mode.php, and you are back to the state you were in before Tracedown was involved. -
Does it deactivate my plugins?
-
No. It changes what WordPress loads for one request, for one person. The stored list of active plugins is never modified, which is also why Tracedown complies with the WordPress.org rule that a plugin may not change the activation status of other plugins.
-
Does it work with WP-CLI?
-
Yes, and safe mode never applies to WP-CLI.
wp tracedown status,wp tracedown abort,wp tracedown restoreandwp tracedown nukeare registered from the safe-mode file so they keep working even while the plugin itself is filtered out of the active list. -
Multisite?
-
Refused in this version, with a message explaining why. Network, site and subsite activation are three separate states and a partial implementation would be worse than none.
Reviews
There are no reviews for this plugin.
Contributors & Developers
“Tracedown Culprit Finder” is open source software. The following people have contributed to this plugin.
Contributors
Translate “Tracedown Culprit Finder” into your language.
Interested in development?
Browse the code, check out the SVN repository, or subscribe to the development log by RSS.
Changelog
0.1.0
- First release.