
Description
PrivacyScrubber ZTDS Guard (Plane 6 of the PrivacyScrubber ecosystem) enforces the Zero-Trust Data Sanitization (ZTDS™ RFC v1.0) protocol for WordPress form privacy, PII redaction, and client-side data masking on contact, patient intake, legal consultation, and financial onboarding forms.
When a visitor submits a form on your WordPress site, sensitive personal data (PII) and protected health information (PHI) frequently flow into third-party webhooks (Zapier, Make, n8n), CRM systems (HubSpot, Salesforce, Pipedrive), email notifications, Slack channels, and AI triage bots (OpenAI ChatGPT, Anthropic Claude, Google Gemini). PrivacyScrubber ZTDS Guard intercepts the form submission inside the visitor’s browser RAM (under 0.4ms) during the DOM capture phase—before fetch() or XMLHttpRequest sends data over the network.
Dual-Envelope Architecture
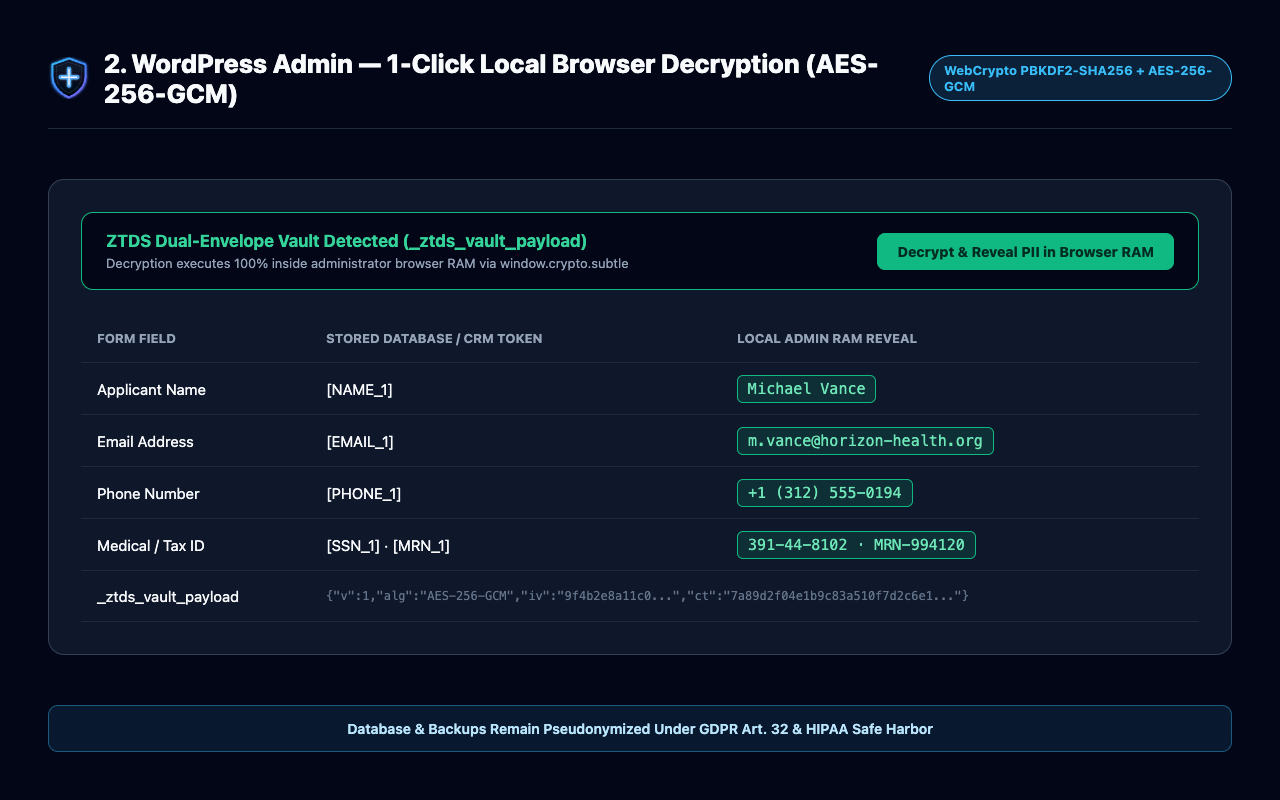
- Public Envelope (Sanitized Form Fields): Sensitive identifiers (Names, Phone Numbers, Emails, Payment Cards, SSN/National IDs, IBANs, Medical Record Numbers, Tax IDs) are replaced in-memory with deterministic tokens such as
[NAME_1],[PHONE_1],[EMAIL_1], and[SSN_1]. Downstream CRMs, email notifications, and AI triage agents process the inquiry with zero exposure to raw PII/PHI. - Private Vault Envelope (
_ztds_vault_payload): The original cleartext mapping is encrypted inside the visitor’s browser using native WebCrypto (AES-256-GCM+PBKDF2-SHA256) and attached as a sealed hidden payload. Authorized administrators can decrypt and reveal original entries in 1 click inside the WordPress Admin dashboard using their local browser key.
Supported Form Builders
- Contact Form 7 (
form.wpcf7-form) - WPForms (
form.wpforms-form) - Elementor Forms (
form.elementor-form) - Gravity Forms (
.gform_wrapper form,form[id^="gform_"]) - Fluent Forms (
form.fluentform) - Custom HTML / AJAX Forms (via
data-ztds="true"or custom CSS selectors in Settings)
Key Architectural Guarantees
- Zero External Network Egress: 100% of detection, tokenization, and encryption executes locally in the visitor’s browser (
window.crypto.subtle). Zero bytes of form content are ever transmitted to PrivacyScrubber or third-party servers. - Fail-Open Business Continuity: If a legacy browser lacks WebCrypto support or encounters a custom DOM exception, the interceptor gracefully bypasses tokenization so your business never loses an inbound lead.
- Statutory Risk Minimization: Technical & Organizational Measure (TOM) supporting GDPR Article 32 pseudonymization, HIPAA Safe Harbor (45 CFR § 164.514(b)), and PCI-DSS v4.0 intake hygiene.
External Services & Privacy Disclosure
This plugin executes 100% locally in the visitor’s browser and does not transmit any form data, visitor PII, or telemetry to any external server. Optional verification badge links to https://privacyscrubber.com/integrations/wordpress/ and https://ztds.ai/ are strictly controlled by the site administrator under Settings -> PrivacyScrubber ZTDS.
Screenshots

AES-256-GCM + PBKDF2-SHA256).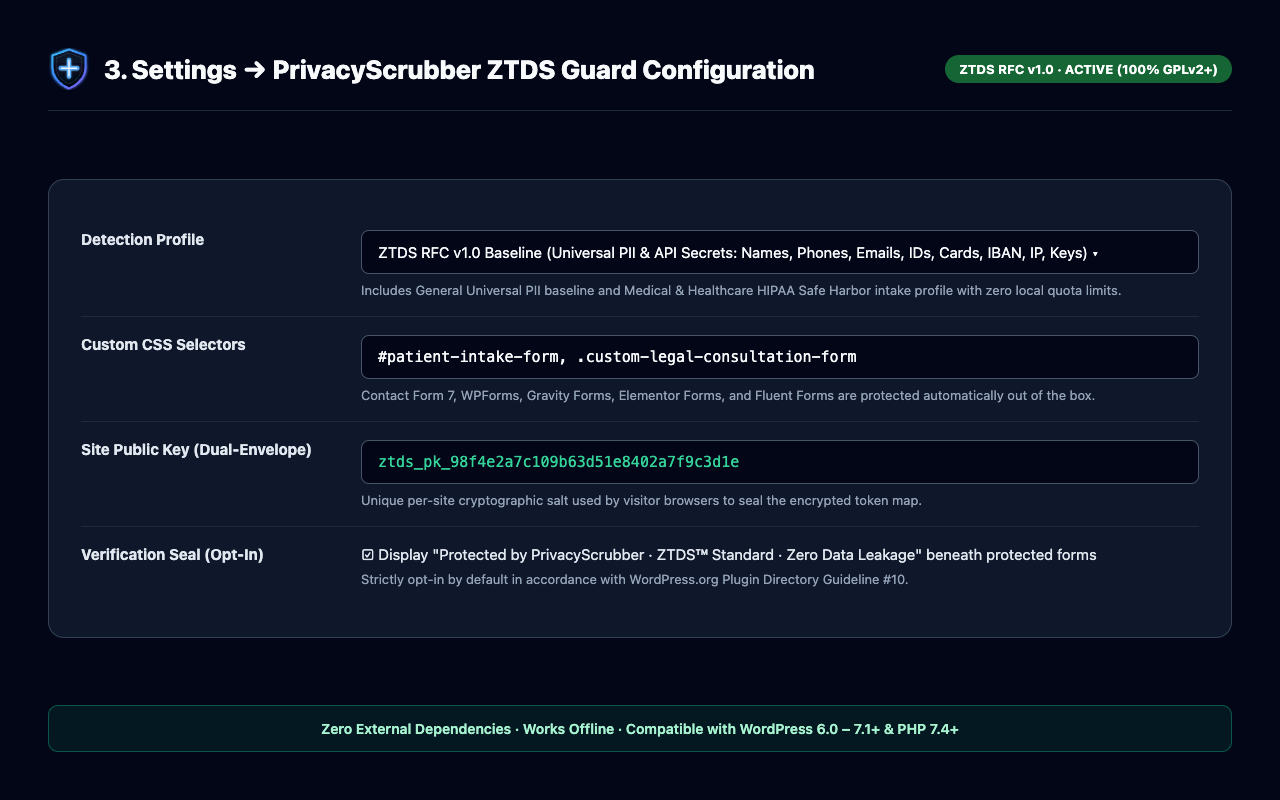
Installation
- Upload the
privacyscrubber-wp-guardfolder to the/wp-content/plugins/directory, or install the plugin ZIP through the WordPress Plugins -> Add New -> Upload Plugin screen. - Activate PrivacyScrubber ZTDS Guard through the Plugins menu in WordPress.
- Navigate to Settings -> PrivacyScrubber ZTDS to select your ZTDS RFC v1.0 baseline profile (
GeneralorMedical), configure custom form selectors, or toggle the verification badge.
FAQ
-
Does this plugin send form submissions to an external API or cloud server?
-
No. All PII detection, token replacement (
[NAME_1],[EMAIL_1]), andAES-256-GCMvault encryption run locally inside the visitor’s web browser (assets/ztds-form-guard.js). No external API requests are made during form submission. -
How do administrators read the original unmasked values?
-
When viewing entries in your WordPress Admin panel,
assets/ztds-admin.jsdetects the_ztds_vault_payloadfield and renders a 1-Click Local Reveal control. Decryption occurs locally in the administrator’s browser memory. -
Are all features in this WordPress plugin unlocked under GPLv2+?
-
Yes. This plugin provides the complete ZTDS RFC v1.0 Reference Form Guard (
Generaluniversal PII/secrets baseline andMedicalintake profile) plus Dual-EnvelopeAES-256-GCMbrowser vaulting 100% free and unrestricted under GPLv2 or later.
Reviews
There are no reviews for this plugin.
Contributors & Developers
“PrivacyScrubber ZTDS Guard — GDPR & HIPAA Form Privacy, PII Redaction & Data Masking” is open source software. The following people have contributed to this plugin.
Contributors
Interested in development?
Browse the code, check out the SVN repository, or subscribe to the development log by RSS.
Changelog
2.4.8
- Synchronized ZTDS RFC v1.0 reference baseline engine with v2.4.8.
- Added dual-authority ZTDS verification seal with independent administrator toggles for badge visibility and verification links (opt-in by default per WordPress.org Guideline 10).
- Added native Gravity Forms (
form[id^="gform_"]) selector support. - Streamlined profile selector to the two native standalone ZTDS RFC v1.0 reference profiles (
GeneralandMedical) with zero local quota restrictions under GPLv2+.
2.4.2
- Initial public release of Plane 6 WordPress ZTDS Form Guard with Dual-Envelope WebCrypto (
AES-256-GCM) vaulting.