

Description
Beziworld – Cookie Consent runs entirely on your own server. It scans your site, recognises services and cookies with a built-in database, holds back scripts, frames and pixels until the visitor agrees, shows a banner with the rules of the visitor’s region and keeps a proof of every decision. No account, no external scanner, no banner loaded from a third-party CDN, no page-view or page limits.
Scanner without external services
- The server crawls the site as a first-time visitor: home, posts, pages, shop, product, cart, checkout, My Account, archives, pages with forms and search. It reads scripts, inline snippets, iframes, pixels, stylesheets, resource hints and Set-Cookie headers.
- A browser scanner for administrators reports what scripts set in the browser (cookie, localStorage, sessionStorage and IndexedDB names, requested domains). No values and no personal data are sent.
- Services are recognised with a local signature database (GA4, GTM, Google Ads, AdSense, Meta Pixel, TikTok, LinkedIn, Pinterest, Microsoft UET and Clarity, Hotjar, Matomo, YouTube, Vimeo, Google Maps, reCAPTCHA, Turnstile, Stripe, PayPal, Przelewy24, WooCommerce, Jetpack, Mailchimp, HubSpot, Klaviyo, live chats and many more) and the Open Cookie Database bundled with the plugin.
- Unknown hosts and cookies are listed for review; you assign a category in one click. Scheduled scans and a notice when something new appears.
- Resources that send the IP address to third parties without cookies are reported too: Google Fonts, the WordPress emoji CDN, Gravatar, font and library CDNs, video and map embeds.
Blocking before consent
- The page HTML is rewritten on the server: scripts get type=”text/plain” with their category, keeping src, async, defer, module type and the original order; iframes become placeholders; tracking pixels, avatars and stylesheets of blocked services wait. The HTML is the same for every visitor, so page caches keep working.
- Scripts and iframes injected later by other scripts are held back too (createElement, appendChild, insertBefore and a MutationObserver).
- After consent everything is restored without reloading the page, in the original order. Withdrawing consent deletes the cookies of the category (also on parent domains) and reloads the page when needed.
- Safe mode (default) reports unknown external scripts; strict mode blocks every unknown script from another domain. Scripts of WordPress, the theme and plugins on your domain are never blocked unless they match a tracking signature.
- Necessary services (payment gateways, CAPTCHA on forms, WooCommerce, library CDNs) are never blocked.
- Placeholders for YouTube, Vimeo and maps use a generic graphic or, when you switch on thumbnail downloads, a preview image stored on your server, never an image from the video platform before consent.
- Optionally, Google Fonts found on the site are copied to your server and served locally from then on (switch it on in the settings or click “Host locally” in the Tools tab); switch off the emoji CDN and hold back Gravatar.
- Manual mode for developers: add data-bwcc-category to a script or iframe that is already in your theme markup and the plugin delays it until consent (data-bwcc-ignore excludes one). The plugin never stores script or HTML code: there are no code fields in its settings.
- Consent gate (the [bwcc_block] shortcode or the Consent gate block): text and images shown after consent, plus an optional YouTube, Vimeo or Google Maps embed that the plugin builds from the URL you enter. Gated content is filtered like post content, so scripts, iframes and custom HTML are removed.
Banner and preference centre
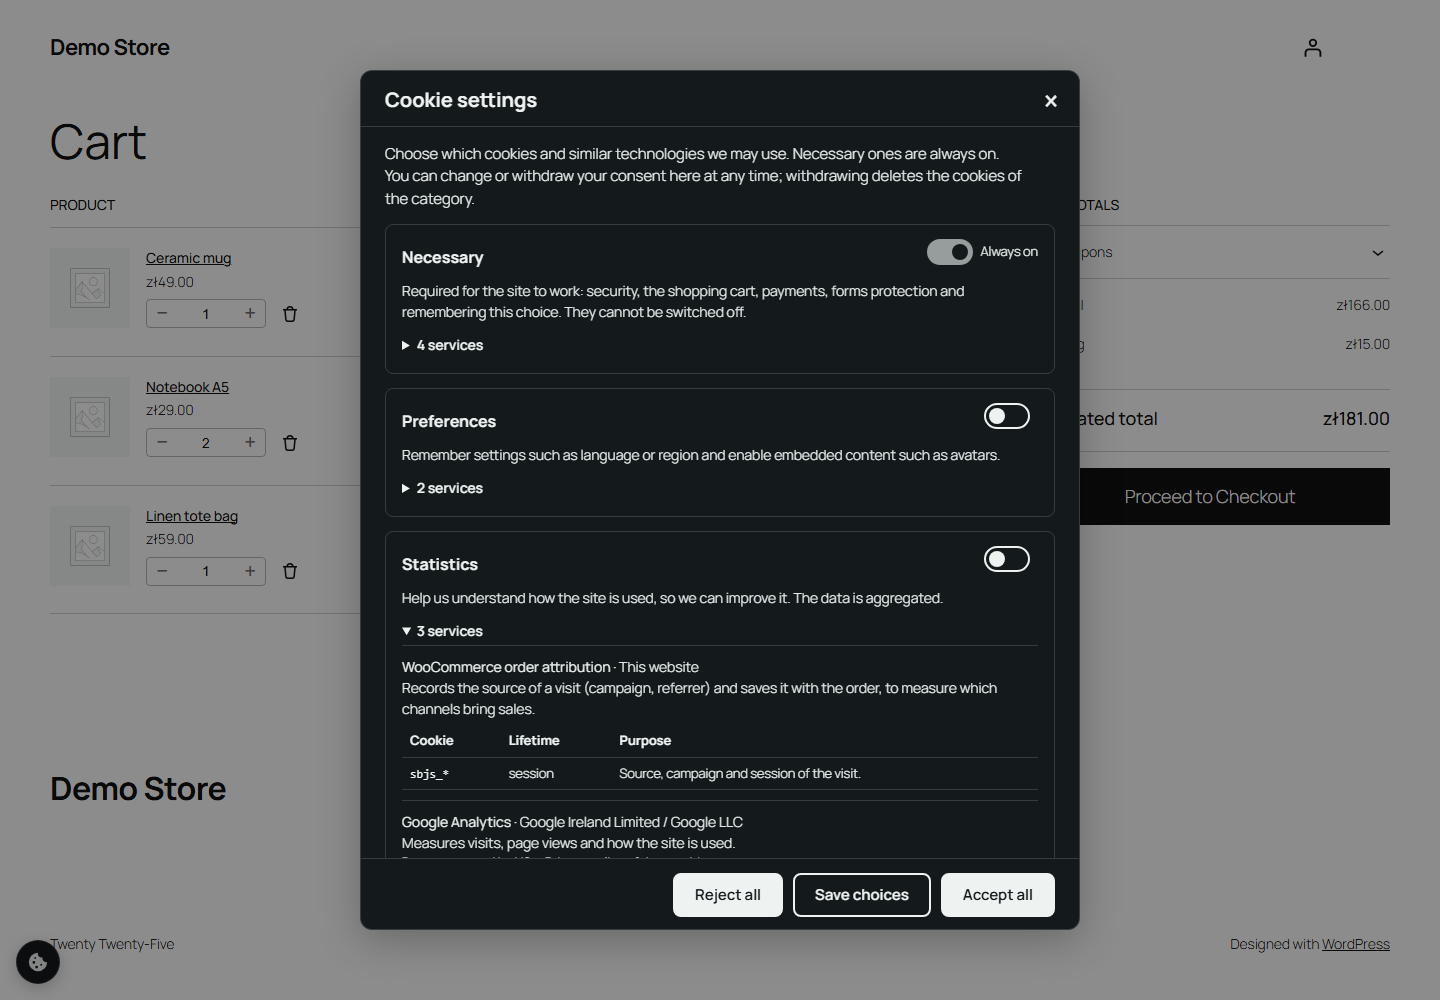
- “Accept all”, “Reject all” and “Settings” on the first layer with the same visual weight; categories without pre-ticked boxes; services and cookies with provider, purpose, lifetime and country on the second layer.
- A permanent settings button, a “Cookie settings” link for menus (#bwcc-settings), a shortcode and a block, and the “Your Privacy Choices” link with the official icon in US opt-out regions.
- Bar, corner box or dialog; light, dark or automatic theme; colours from theme.json or your own with a contrast check; live preview.
- Accessible (WCAG 2.2 AA goal): keyboard operation, focus trap only in the dialog, ARIA, switches with role=”switch”, reduced motion, no scroll lock by default, no layout shift, the banner comes first in the tab order and never hides the focused element.
- Small: no jQuery, no external requests; the banner script loads deferred and the stylesheet does not block rendering. Hidden from search engine crawlers without changing the page content.
- Every text is translatable and a Polish translation is included; custom texts work with WPML and Polylang string translation.
Laws of every region
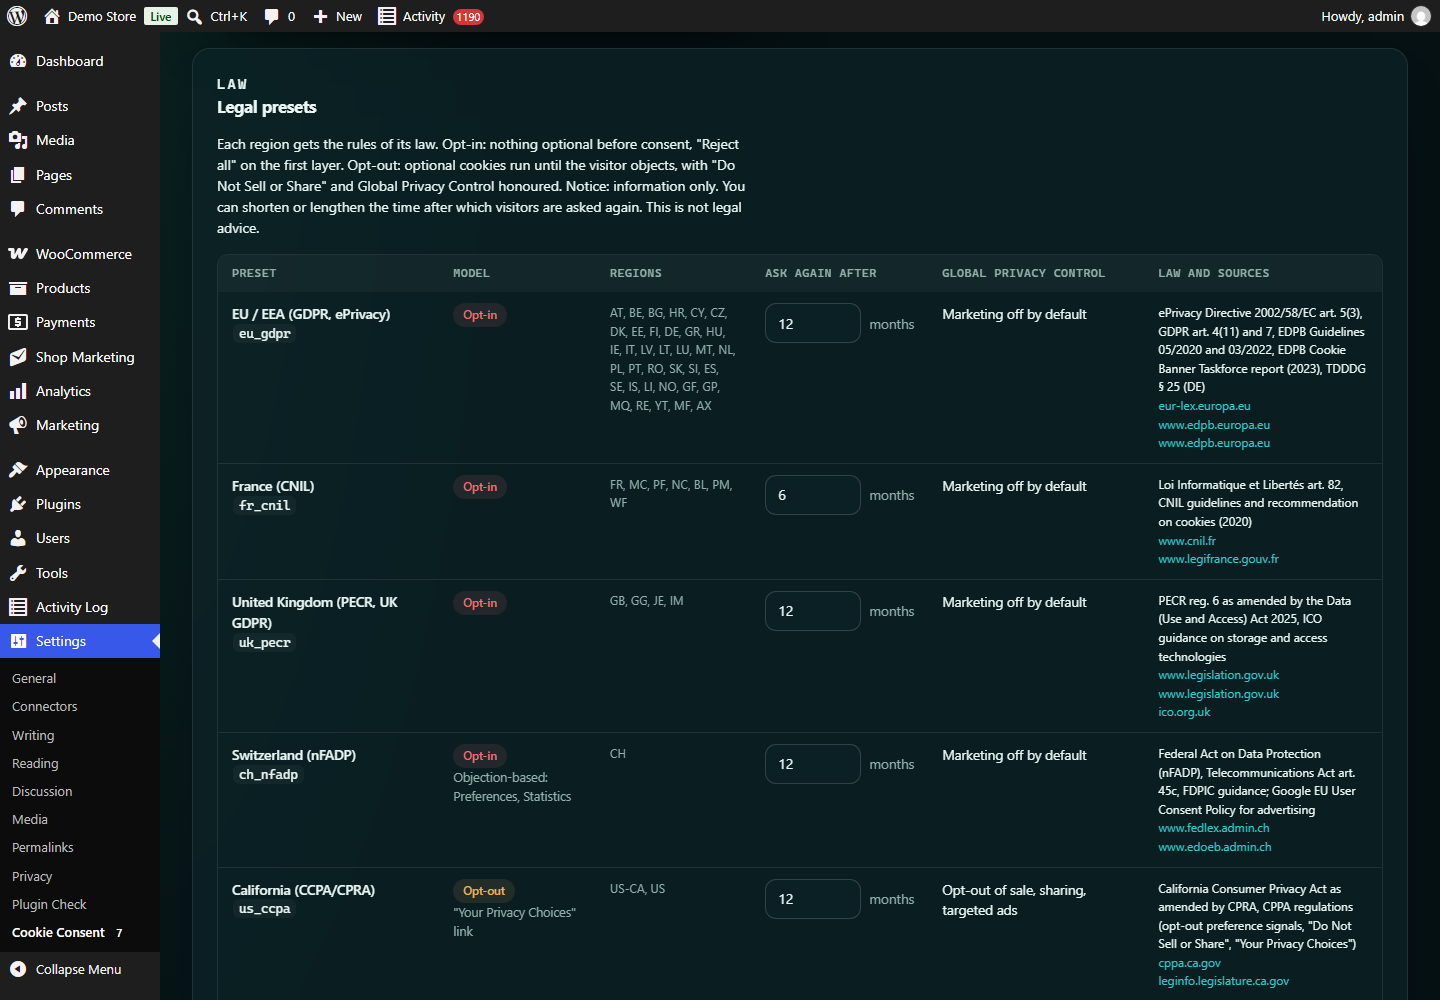
Legal presets map countries and US states to the rules of their law: GDPR and ePrivacy (EU/EEA, with 6-month validity for France/CNIL and 12 months elsewhere), UK PECR, Swiss nFADP, CCPA/CPRA and the other US state laws (opt-out with Global Privacy Control), Quebec Law 25, PIPEDA, LGPD, APPI, PIPA, PIPL, DPDP, Australia, New Zealand, POPIA, KVKK, Israel and notice-only regions. Unknown regions get the strictest opt-in rules.
- Region detection without external services: CDN headers (Cloudflare, CloudFront, Vercel, Fastly, Akamai or your own list) or a local MMDB database you upload (GeoLite2, GeoIP2, IP2Location), read by the plugin itself.
- Detection happens in the browser through a small, never-cached endpoint, so full page caching keeps working. The device time zone can only make the rules stricter.
- Global Privacy Control is honoured as an opt-out of sale, sharing and targeted advertising in US regions, and switches marketing off in consent regions.
- Consent is asked again after the period of the preset, after you raise the policy version and, optionally, when a new service joins a category the visitor accepted.
This plugin helps you comply; it is not legal advice.
Google, GTM and other platforms
- Google Consent Mode v2: consent default as the first script of the head (before GTM and gtag) with the stored choice of returning visitors, regional defaults, wait_for_update, ads_data_redaction and url_passthrough; consent update after every decision. Basic mode (tags wait) or advanced mode (tags load with denied consent).
- Google Tag Manager: bwcc_consent_default and bwcc_consent_update dataLayer events for the Consent Initialization trigger, optional container.
- WP Consent API, used by WooCommerce, Site Kit and others. WooCommerce order attribution (sbjs cookies) is treated as statistics.
- Microsoft UET consent mode and Clarity consent API, Meta Pixel, TikTok Pixel, Matomo and Hotjar adapters.
- Warning when another consent plugin is active.
Proof of consent
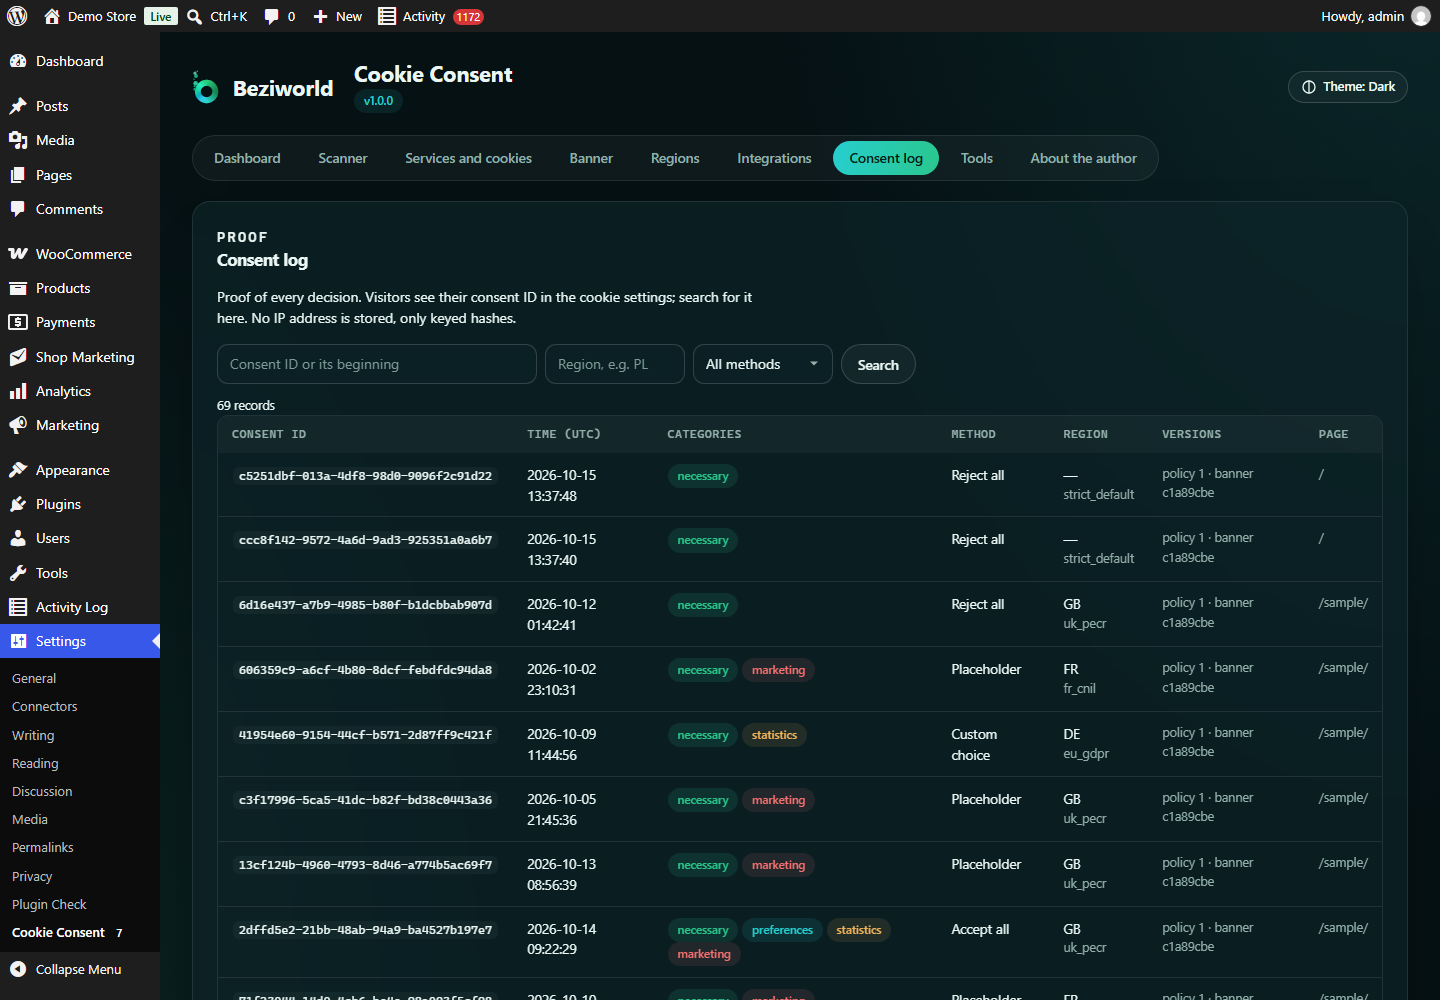
- Local consent log: random consent ID (shown to the visitor), time, versions of the policy and the banner, categories, region, method (click, GPC, placeholder), keyed hashes of the IP address and the browser instead of the values.
- Search by consent ID, CSV export, statistics per region, configurable retention, personal data export and erasure for logged-in users.
- The consent cookie is signed (HMAC), so PHP can trust it: bwcc_has_consent( ‘statistics’ ).
Documents and tools
- Cookie declaration generated from the scan (shortcode and block) and a suggested privacy policy text.
- Setup wizard, diagnostics and a before-consent check that loads your pages as a first-time visitor from the EU and lists every cookie, script, frame and third-party request with an OK or “to fix” status. It also runs after every scan.
- WP-CLI: wp bwcc scan, services, consents, export, import, diagnose and reconsent. REST API with permissions. JSON export and import. Multisite with per-site or shared settings.
External services
Out of the box the plugin does not contact any external service, does not load fonts, stylesheets, scripts or images from other servers and sends no data anywhere. The banner, its script, stylesheet and images are served from your own site. Each service below is contacted only after you, the site owner, switch on or configure the related feature.
Google Tag Manager (optional container)
- What and why: when you enter a GTM container ID in Integrations, the plugin adds the Google Tag Manager container to your pages so that your tags can run.
- When: in the default (basic) Consent Mode the container stays inert and is loaded only after the visitor accepts the statistics or the marketing category. Only if you choose the advanced Consent Mode does it load before the decision, with all consent signals set to “denied”.
- Data: the visitor’s browser requests https://www.googletagmanager.com/gtm.js with your container ID; Google receives the visitor’s IP address, browser data and the page address.
- Terms: https://marketingplatform.google.com/about/analytics/tag-manager/use-policy/ and https://policies.google.com/terms. Privacy policy: https://policies.google.com/privacy
YouTube, Vimeo and Google Maps (consent gate embeds)
- What and why: when you enter a video or map URL in the Consent gate block or the [bwcc_block] shortcode, the plugin shows that video or map.
- When: only after the visitor accepts the category of the gate (or clicks “Load and accept”). Nothing is loaded before that.
- Data: the visitor’s browser loads the player or the map from www.youtube-nocookie.com, player.vimeo.com (with the do-not-track parameter) or www.google.com/maps; the provider receives the IP address, browser data and may set cookies.
- YouTube terms: https://www.youtube.com/t/terms Google privacy policy: https://policies.google.com/privacy Vimeo terms: https://vimeo.com/terms Vimeo privacy policy: https://vimeo.com/privacy Google Maps terms: https://policies.google.com/terms
Video thumbnails (optional, off by default)
- What and why: when you switch on “Download video thumbnails during the scan”, placeholders of embedded videos show a preview image stored on your server instead of a grey graphic.
- When: only during a scan you start or schedule, for videos the scan finds on your site.
- Data: your server (not the visitor’s browser) downloads https://i.ytimg.com/vi/VIDEO_ID/hqdefault.jpg for YouTube and asks https://vimeo.com/api/oembed.json for the Vimeo preview address. Only the public video ID is sent; no visitor data.
- YouTube terms: https://www.youtube.com/t/terms Google privacy policy: https://policies.google.com/privacy Vimeo terms: https://vimeo.com/terms Vimeo API terms: https://vimeo.com/legal/service-terms/api Vimeo privacy policy: https://vimeo.com/privacy
Google Fonts (optional, off by default)
- What and why: when you switch on “Serve hosted Google Fonts locally” or click “Host locally” in Tools, the plugin copies Google Fonts that your theme or plugins already use to your server, so visitors no longer contact Google for them.
- When: once per stylesheet, after you switch the option on or click the button.
- Data: your server (not the visitor’s browser) downloads the stylesheet from fonts.googleapis.com and the font files from fonts.gstatic.com. No visitor data is sent.
- Terms: https://developers.google.com/terms Privacy: https://developers.google.com/fonts/faq/privacy and https://policies.google.com/privacy
Not external services
- Region detection reads the country header of your own CDN or proxy, or a MaxMind/IP2Location MMDB file that you upload yourself. No geolocation API is called and no database is downloaded.
- The scanner, the before-consent check and the browser scanner only request pages and endpoints of your own site.
- The admin screens contain plain links to the plugin home page (beziworld.eu) and, when AdSense is found, to the Google AdSense help centre (support.google.com). Nothing is requested from these sites.
Bundled reference data (no connection is made)
The folder data/ holds an offline reference database that ships with the plugin and changes only with plugin releases. It is never downloaded, updated or synchronised at run time, and the plugin never sends a request to any host or address it contains. Automated scans may report these files as remote calls or third-party services; they are lookup tables, not network code.
- data/services.php lists third-party services with the host names their scripts, frames, images and stylesheets use. The plugin compares these names with the markup of your own pages so that it can recognise a service your site already embeds and hold it back until the visitor consents. The privacy policy address of each service is printed as a plain link in the admin screens and in the cookie declaration, for your visitors to read.
- data/open-cookie-database.php contains more than 2,200 cookie names with their purpose, retention and data controller, plus the privacy policy addresses of those controllers (stored once each), from the Open Cookie Database by Jaap Kwakman and contributors (https://github.com/jkwakman/Open-Cookie-Database), Apache License 2.0. The plugin matches the names with cookies found on your site and prints the descriptions and privacy links in the admin screens and the cookie declaration. It is loaded only in the admin, during scans and in WP-CLI.
- data/presets.php holds the legal presets of the regions, with links to the official texts of the laws and guidelines, shown as plain links in the Regions tab.
Every host name that appears in these files is listed in the FAQ under “Which third-party host names appear in the bundled data?”.
Credits
Cookie descriptions include data from the Open Cookie Database by Jaap Kwakman and contributors (https://github.com/jkwakman/Open-Cookie-Database), licensed under the Apache License, Version 2.0 (https://www.apache.org/licenses/LICENSE-2.0). A copy of the licence is included in data/LICENSE-open-cookie-database.txt. The data was modified: it was converted from CSV to a PHP array, long descriptions were shortened and categories were mapped to the categories of this plugin. The data is used only for local lookups; the plugin never requests the database or any address listed in it.
Screenshots





Blocks
This plugin provides 3 blocks.
- Cookie settings link A link that reopens the cookie settings, so visitors can change or withdraw consent.
- Consent gate Shows text, images and a YouTube, Vimeo or Google Maps embed only after the visitor accepts a cookie category. Scripts and custom HTML are not allowed.
- Cookie declaration Table of the cookies and services used on this site, grouped by category, generated from the scan.
Installation
- Install and activate the plugin.
- Open Settings > Cookie Consent. The wizard asks about regions, scans the site, shows what was found, lets you choose the look and publishes the banner.
- Add the Cookie declaration block (or [bwcc_cookie_declaration]) to your cookie or privacy policy page and a “Cookie settings” link (#bwcc-settings) to the footer menu.
- Clear the page cache.
FAQ
-
Does the plugin send anything to an external service?
-
No. Scanning, classification, geolocation, the banner and the consent log run on your server. See “External services” for the optional features that you can switch on.
-
Can I paste a script or embed code into the consent gate?
-
No. The gate accepts text and images (filtered like post content) and the URL of a YouTube or Vimeo video or a Google Maps embed; the plugin builds the embed itself. To delay a script your theme already prints, add data-bwcc-category=”statistics” (or another category) to its script tag, or add its URL or host to a service in the Services tab.
-
Does it work with page caching?
-
Yes. Every visitor gets the same HTML; the region is detected by the browser through a never-cached endpoint and the decision is made in the browser. Exclude the plugin scripts from “delay JavaScript” options (see Tools > Caching and optimisation).
-
How is the region detected without a geolocation service?
-
From the country header of your CDN or proxy (Cloudflare CF-IPCountry, CloudFront, Vercel, Fastly, Akamai or a header you add) or from a local MMDB database you upload. Without either, every visitor gets the strictest opt-in rules, which is lawful everywhere.
-
Will it break my site?
-
Necessary services, your own scripts and the scripts of WordPress, the theme and plugins are never blocked. Unknown external scripts are only reported in the default safe mode. The before-consent check shows exactly what loads before consent.
-
Can I use it for AdSense?
-
Publishers that show Google ads (AdSense, Ad Manager, AdMob) to visitors in the EEA, the UK and Switzerland must use a consent management platform certified by Google that implements IAB TCF v2.2 and is registered with IAB Europe under its own CMP ID. This plugin is not certified and does not implement TCF, so it is not suitable for serving Google ads in those regions; the plugin warns you when it finds AdSense. Advertisers that use Google Ads conversion tracking or GA4 only need Consent Mode v2, which is fully supported.
-
What does the plugin store about visitors?
-
The plugin itself does not track visitors and sends nothing to third parties.
- Cookies: only the two necessary first-party cookies described in “Where are the cookies of the plugin?” (bwcc_consent after a decision, bwcc_region for the browser session). No identifiers are created before the visitor decides, apart from the random consent ID generated when the decision is saved.
- Before a decision the browser only asks your own site for the region (/wp-json/bwcc/v1/geo). Third-party scripts, frames, pixels and the optional GTM container wait for consent.
- Consent log (can be switched off in Settings): for each decision it stores the random consent ID, the time, the policy and banner versions, the chosen categories, the region and legal preset, the method (button, GPC signal, placeholder), whether GPC was sent, the path of the page (without the query string), the user ID for logged-in users, and keyed hashes (HMAC with a secret of your site) of the IP address and the browser user agent. The IP address and the user agent themselves are never stored. Records are deleted after the retention period you choose (24 months by default) and can be exported or erased with the WordPress personal data tools for logged-in users.
- Rate limiting of the public consent endpoint uses a short-lived keyed hash of the IP address, never the address itself.
- The browser scanner reports only names of cookies and storage keys and requested host names, never values, to your own site. For visitors it is off by default.
- A suggested text for your privacy policy is added to Settings > Privacy.
-
Can developers extend the plugin?
-
Every part can be extended: legal presets, geolocation providers, signature sources, integration adapters, categories, scanner sources, the consent log storage and a consent framework interface prepared for IAB TCF. PHP hooks (bwcc/loaded, bwcc/is_pro, bwcc/blocking/decision, bwcc/regions/preset, bwcc/consent/valid and many more), a JavaScript API (window.bwcc.getConsent(), setConsent(), open(), onChange()) and the bwcc:ready and bwcc:consent events. All front-end output comes from templates you can override in yourtheme/beziworld-cookie-consent/. See docs/developers.md in the plugin folder.
-
Which third-party host names appear in the bundled data?
-
None of these hosts is contacted by the plugin. They are offline reference data (see “Bundled reference data” under “External services”).
Host names of services recognised in your pages (data/services.php, used only for matching):
- Stripe: js.stripe.com, m.stripe.network, m.stripe.com, hooks.stripe.com, api.stripe.com
- PayPal: paypal.com/sdk, www.paypalobjects.com, paypal.com/tagmanager, c.paypal.com, www.paypal.com/smart
- Przelewy24: przelewy24.pl
- Tpay: tpay.com, secure.tpay.com
- PayU: secure.payu.com, secure.snd.payu.com, static.payu.com
- Google reCAPTCHA: google.com/recaptcha, www.gstatic.com/recaptcha, recaptcha.net
- Cloudflare Turnstile: challenges.cloudflare.com
- hCaptcha: hcaptcha.com, js.hcaptcha.com
- Public library CDN: cdn.jsdelivr.net, cdnjs.cloudflare.com, unpkg.com, code.jquery.com, ajax.googleapis.com
- Google Fonts: fonts.googleapis.com, fonts.gstatic.com
- WordPress emoji (s.w.org): s.w.org/images/core/emoji
- Gravatar: gravatar.com, secure.gravatar.com, 0.gravatar.com, 1.gravatar.com, 2.gravatar.com
- Adobe Fonts: use.typekit.net, p.typekit.net
- Font Awesome CDN: kit.fontawesome.com, use.fontawesome.com, ka-f.fontawesome.com
- Bunny Fonts: fonts.bunny.net
- Google Tag Manager: googletagmanager.com/gtm.js, googletagmanager.com/ns.html
- Google Analytics: googletagmanager.com/gtag/js, google-analytics.com, analytics.google.com, region1.google-analytics.com, stats.g.doubleclick.net
- Google Ads: googletagmanager.com/gtag/js?id=AW-, googleadservices.com, googleads.g.doubleclick.net, ad.doubleclick.net, www.google.com/pagead, google.com/ads/ga-audiences
- Google AdSense: pagead2.googlesyndication.com, tpc.googlesyndication.com, googlesyndication.com, adservice.google.com, fundingchoicesmessages.google.com
- Meta Pixel / Facebook SDK: connect.facebook.net, facebook.com/tr, www.facebook.com/plugins
- TikTok Pixel: analytics.tiktok.com
- LinkedIn Insight Tag: snap.licdn.com, px.ads.linkedin.com, dc.ads.linkedin.com
- Pinterest Tag: s.pinimg.com/ct, ct.pinterest.com
- Microsoft Advertising (UET): bat.bing.com, bat.bing.net
- Microsoft Clarity: clarity.ms, www.clarity.ms
- Hotjar: static.hotjar.com, script.hotjar.com, hotjar.io, hotjar.com
- Matomo: matomo.cloud, cdn.matomo.cloud
- Jetpack Stats: stats.wp.com, pixel.wp.com
- Plausible Analytics: plausible.io/js
- Cloudflare Web Analytics: static.cloudflareinsights.com, cloudflareinsights.com/cdn-cgi/rum
- Yandex Metrica: mc.yandex.ru, mc.yandex.com
- Smartlook: smartlook.com, rec.smartlook.com, web-sdk.smartlook.com
- Mouseflow: cdn.mouseflow.com, mouseflow.com
- X (Twitter) Pixel: static.ads-twitter.com, analytics.twitter.com, t.co/i/adsct, ads-api.twitter.com
- Snap Pixel: sc-static.net, tr.snapchat.com
- Reddit Pixel: redditstatic.com/ads, alb.reddit.com
- Criteo: static.criteo.net, criteo.com, criteo.net
- HubSpot: js.hs-scripts.com, js.hs-analytics.net, js.hsadspixel.net, js.hs-banner.com, track.hubspot.com
- Mailchimp: chimpstatic.com, list-manage.com/subscribe
- Klaviyo: static.klaviyo.com, static-tracking.klaviyo.com, a.klaviyo.com
- GetResponse: ga.getresponse.com, app.getresponse.com/view_webform, getresponse-cdn.com
- SALESmanago: salesmanago.com, salesmanago.pl
- edrone: edrone.me, api.edrone.me
- Ceneo: ssl.ceneo.pl, ceneo.pl/shops
- YouTube: youtube.com/embed, youtube-nocookie.com, youtube.com/iframe_api, youtube.com/player_api, youtube.com/s/player, youtu.be, i.ytimg.com, ytimg.com
- Vimeo: player.vimeo.com, vimeo.com/api, vimeocdn.com
- Google Maps: google.com/maps, maps.google.com, maps.googleapis.com, maps.gstatic.com
- OpenStreetMap: openstreetmap.org/export/embed, tile.openstreetmap.org
- Spotify: open.spotify.com/embed
- SoundCloud: w.soundcloud.com
- Instagram: instagram.com/embed.js, www.instagram.com/p/, instagram.com/embed
- X (Twitter) embeds: platform.twitter.com, platform.x.com, syndication.twitter.com
- TikTok embeds: tiktok.com/embed, www.tiktok.com/embed.js
- Disqus: disqus.com/embed.js, disquscdn.com, disqus.com
- ShareThis: platform-api.sharethis.com, buttons-config.sharethis.com, sharethis.com
- Trustpilot: widget.trustpilot.com, invitejs.trustpilot.com
- Calendly: assets.calendly.com, calendly.com
- tawk.to: embed.tawk.to, tawk.to
- Smartsupp: smartsuppchat.com, smartsupp.com, smartsuppcdn.com
- Intercom: widget.intercom.io, js.intercomcdn.com
- Crisp: client.crisp.chat
- Zendesk: static.zdassets.com, ekr.zdassets.com
- LiveChat: cdn.livechatinc.com, livechatinc.com
Hosts of the privacy policy links of these services (data/services.php, printed as plain links): automattic.com, bunny.net, calendly.com, crisp.chat, edrone.me, fontawesome.com, help.disqus.com, legal.hubspot.com, legal.trustpilot.com, matomo.org, mouseflow.com, osmfoundation.org, plausible.io, poland.payu.com, policies.google.com, policy.pinterest.com, privacy.microsoft.com, sharethis.com, soundcloud.com, stripe.com, tpay.com, values.snap.com, vimeo.com, wordpress.org, www.adobe.com, www.ceneo.pl, www.cloudflare.com, www.criteo.com, www.facebook.com, www.getresponse.com, www.hcaptcha.com, www.hotjar.com, www.intercom.com, www.intuit.com, www.jsdelivr.com, www.klaviyo.com, www.linkedin.com, www.livechat.com, www.paypal.com, www.przelewy24.pl, www.reddit.com, www.salesmanago.com, www.smartlook.com, www.smartsupp.com, www.spotify.com, www.tawk.to, www.tiktok.com, www.zendesk.com, x.com, yandex.com.
Hosts of the privacy policy links of cookie controllers (data/open-cookie-database.php, printed as plain links): 33across.com, ablyft.com, about.ads.microsoft.com, account.microsoft.com, adcalls.com, adhese.com, adkernel.com, admixer.net, adsrvr.org, amazon.com, amplitude.com, automattic.com, aws.amazon.com, bidence.com, bitly.com, blog.codepen.io, bombora.com, borlabs.io, business.safety.google, cakephp.org, casalemedia.com, channel.me, chartbeat.com, cheq.ai, claritas.com, cleantalk.org, codeigniter.com, community.marfeel.com, complianz.io, contentsquare.com, cookie-script.com, cookiefirst.com, craftcms.com, crisp.chat, customer.io, datadome.co, developer.mediarithmics.io, dfactory.co, digitalaudience.io, docs.djangoproject.com, docs.github.com, docs.inspectlet.com, docs.parse.ly, dotmetrics.net, e-volution.ai, equativ.com, exponea.com, foundation.wikimedia.org, getblue.io, getflowbox.com, github.com, gumgum.com, help.disqus.com, help.twitter.com, hu-manity.co, id5.io, issuu.com, justpremium.com, kompare.io, legal.epsilon.com, legal.hubspot.com, legal.mailmunch.com, legal.rdstation.com, legal.yahoo.com, livehelperchat.com, liveramp.com, mailchimp.com, matomo.org, maxlead.com, mixpanel.com, mopinion.com, nextjs.org, nexx360.io, optinmonster.com, osano.trusthub.com, partnerize.com, permutive.com, piano.io, piwik.pro, platform-cdn.sharethrough.com, platform161.com, plausible.io, policy.pinterest.com, polylang.pro, postviewscounter.com, prebidprd.wpengine.com, privacy.baidu.com, privacy.console.didomi.io, privacy.google.com, privacypillar.com, pubmatic.com, pulsepoints-new-website.webflow.io, richaudience.com, rtbhouse.com, rubiconproject.com, sharethis.com, sharpspring.com, shopping.groovinads.com, site.adform.com, siteimprove.com, sleeknote.com, snapengage.com, snapwidget.com, snowplowanalytics.com, sonobi.com, squeezely.tech, stape.io, stonly.com, stripe.com, support.wix.com, swym.it, termly.io, tripadvisor.mediaroom.com, triplelift.com, twitter.com, typo3.org, umami.is, underdogmedia.com, usefathom.com, vercel.com, verve.com, viafoura.com, vimeo.com, vwo.com, weborama.com, wisepops.com, wistia.com, wordpress.org, wp-glogin.com, www.abovomedia.nl, www.abtasty.com, www.activecampaign.com, www.adalyser.com, www.addwebsolution.com, www.adition.com, www.admatic.com.tr, www.adobe.com, www.adyen.com, www.akamai.com, www.algolia.com, www.amazon.com, www.aniview.com, www.awin.com, www.axept.io, www.bazaarvoice.com, www.beeswax.com, www.belco.nl, www.beslist.nl, www.blueconic.com, www.braze.com, www.citrix.com, www.civicuk.com, www.cloudflare.com, www.cognitoforms.com, www.commandersact.com, www.comscore.com, www.consentmanager.net, www.constantcontact.com, www.convert.com, www.cookiebot.com, www.cookieconsent.io, www.cookielawinfo.com, www.cookieyes.com, www.crazyegg.com, www.datatrics.com, www.drift.com, www.drupal.org, www.duda.co, www.dynamicyield.com, www.dynatrace.com, www.easysize.me, www.emetriq.com, www.enzuzo.com, www.ezoic.com, www.facebook.com, www.feedbackcompany.com, www.freewheel.com, www.funda.nl, www.gemius.pl, www.getbeamer.com, www.heap.io, www.home.neustar, www.hotjar.com, www.id5.io, www.imperva.com, www.improvedigital.com, www.indeed.com, www.infonline.de, www.intercom.com, www.internetbrands.com, www.intershop.com, www.iubenda.com, www.jimdo.com, www.kelkoogroup.com, www.kiyoh.nl, www.klaviyo.com, www.laravel.com, www.leadfeeder.com, www.leadinfo.com, www.lightboxcdn.com, www.lightspeedhq.com, www.linkedin.com, www.livechat.com, www.lotame.com, www.luckyorange.com, www.magnite.com, www.media.net, www.mediamath.com, www.mediavine.com, www.mercadolibre.com.ar, www.mooveagency.com, www.nativo.com, www.nielsen.com, www.nopcommerce.com, www.onaudience.com, www.onetrust.com, www.openx.com, www.optimizely.com, www.oracle.com, www.ortecadscience.com, www.outbrain.com, www.ozoneproject.com, www.pangleglobal.com, www.paypal.com, www.perfectaudience.com, www.perl.org, www.personyze.com, www.php.net, www.plesk.com, www.powerlinks.com, www.proprofs.com, www.qualtrics.com, www.quantcast.com, www.radware.com, www.reddit.com, www.redditinc.com, www.roku.com, www.rudderstack.com, www.sailthru.com, www.salesforce.com, www.sap.com, www.seedtag.com, www.semasio.net, www.shopify.com, www.sitespect.com, www.smaato.com, www.snap.com, www.solarwinds.com, www.sooqr.com, www.sovrn.com, www.spotify.com, www.spotx.tv, www.surveymonkey.com, www.taboola.com, www.tapad.com, www.tappx.com, www.tawk.to, www.teads.com, www.tiktok.com, www.totvs.com, www.towerdata.com, www.twiago.com, www.twitch.tv, www.typeform.com, www.undertone.com, www.vidoomy.com, www.vuble.tv, www.webtoffee.com, www.wepublish.com, www.whatsapp.com, www.wunderkind.co, www.zendesk.com, www.zoho.com, xenforo.com, xperience.io, yahoo.com, yandex.com, yieldmo.com, yithemes.com, zeotap.com.
Hosts of the links to laws and guidelines (data/presets.php, printed as plain links in the Regions tab): coag.gov, cppa.ca.gov, eur-lex.europa.eu, iapp.org, ico.org.uk, inforegulator.org.za, leginfo.legislature.ca.gov, portal.ct.gov, www.cai.gouv.qc.ca, www.cnil.fr, www.edoeb.admin.ch, www.edpb.europa.eu, www.fedlex.admin.ch, www.gov.br, www.gov.il, www.kvkk.gov.tr, www.legifrance.gouv.fr, www.legislation.gov.au, www.legislation.gov.uk, www.legislation.govt.nz, www.legisquebec.gouv.qc.ca, www.meity.gov.in, www.npc.gov.cn, www.oaic.gov.au, www.pdpc.gov.sg, www.pipc.go.kr, www.planalto.gov.br, www.ppc.go.jp, www.priv.gc.ca, www.soumu.go.jp.
-
bwcc_consent holds the decision and the consent ID (signed, first-party, SameSite=Lax, Secure on HTTPS, lifetime of the legal preset). bwcc_region holds the detected region for the browser session. Both are necessary. The plugin sets no tracking, analytics or advertising cookies.
Reviews
There are no reviews for this plugin.
Contributors & Developers
“Beziworld – Cookie Consent” is open source software. The following people have contributed to this plugin.
Contributors
Translate “Beziworld – Cookie Consent” into your language.
Interested in development?
Browse the code, check out the SVN repository, or subscribe to the development log by RSS.
Changelog
1.0.5
- Polish translation included: the banner, the preference centre, the cookie declaration, the admin screens and the blocks follow the site language. Language packs from translate.wordpress.org take precedence when available.
- The dashboard shows the result of the latest before-consent check, also when the check was run after the last scan.
- The names and notes of the remaining legal presets can be translated.
1.0.4
- The service catalogue stores the Cloudflare privacy policy address once.
1.0.3
- Admin screens escape every value at the point of output; badges and category selects are printed by dedicated escaping methods.
- The head bootstrap is printed with wp_print_inline_script_tag(); integrations extend it through the new bwcc/head_scripts filter, which replaces bwcc/head_markup.
- The consent log CSV export is written with fputcsv().
- The bundled Open Cookie Database no longer stores the unused domain column and keeps each privacy policy address once.
- Documented the bundled reference data and every host name it recognises; the privacy, developer and IAB TCF notes moved to the FAQ.
1.0.2
- The consent gate accepts only content allowed in posts plus a YouTube, Vimeo or Google Maps URL; the plugin builds the embed itself and never runs scripts from gated content.
- Held iframes of placeholders are filtered on output.
- Request data is read key by key and sanitised before it reaches filters and geolocation providers.
- Inline configuration uses the default JSON escaping.
- The optional Google Tag Manager container waits for consent in the basic Consent Mode.
- Google Fonts and video thumbnail downloads are now opt-in.
- Documented every external service and the privacy of the consent log.
1.0.1
- Fixed saving settings on multisite installations that share the main site’s configuration.
- Added safe support for alpha colours in 4/8-digit hex and rgba() formats.
- Improved the colour editor, live preview, field visibility and save error feedback.
- Bound each settings nonce to its exact section and field list.
1.0.0
- First release.