Description
The connector for Culpritly: this plugin runs inside your store and reports to your Culpritly account. Culpritly tells WooCommerce store owners and membership site owners what changed, what broke, and what to undo.
This plugin needs a Culpritly account. It is a connector for the hosted Culpritly service, not a stand-alone tool. A Culpritly account starts with a 14 day free trial (no card needed, one store); after the trial the service is a paid subscription. The plugin itself is free, contains no locked or time-limited features, and all of its code is in this package under the GPL. Until you paste a site key and secret from your Culpritly account into the plugin settings, the plugin does not contact any server and does not record anything.
What the connector records once you have connected it:
- Plugin, theme and WordPress core updates (old and new version, manual or automatic).
- Plugin installs, activations and deactivations, and theme switches.
- Changes to key settings: WooCommerce settings, payment gateway settings, permalinks and common cache plugins. Only the option name and which keys changed are recorded, never the values.
- Saves from the built-in plugin and theme file editor (the file path only).
- PHP fatal errors, mapped to the plugin or theme they came from.
- JavaScript errors on payment pages: message, script path, line and column, mapped to the plugin or theme that served the script. Payment pages are the WooCommerce cart and checkout, the signup and billing pages of Restrict Content Pro, MemberPress and Paid Memberships Pro, and any path you add under “Extra payment pages”.
- Payment scripts that fail to load on those pages (Stripe, PayPal, Braintree, Square).
- Error pages shown when a payment page form post is stopped with wp_die(), for example “Missing Stripe setup intent”. The page the visitor sees is not changed.
- Order signals: order created, paid and failed, with totals, currency and gateway only.
- A daily snapshot of WordPress, WooCommerce and PHP versions, installed plugins, whether each plugin updates automatically, and your checkout type and enabled payment gateways.
- Once, right after you connect: the number of paid orders and their total for each of the last 60 days. Dates, counts and totals only; no order ids, customers, products or addresses.
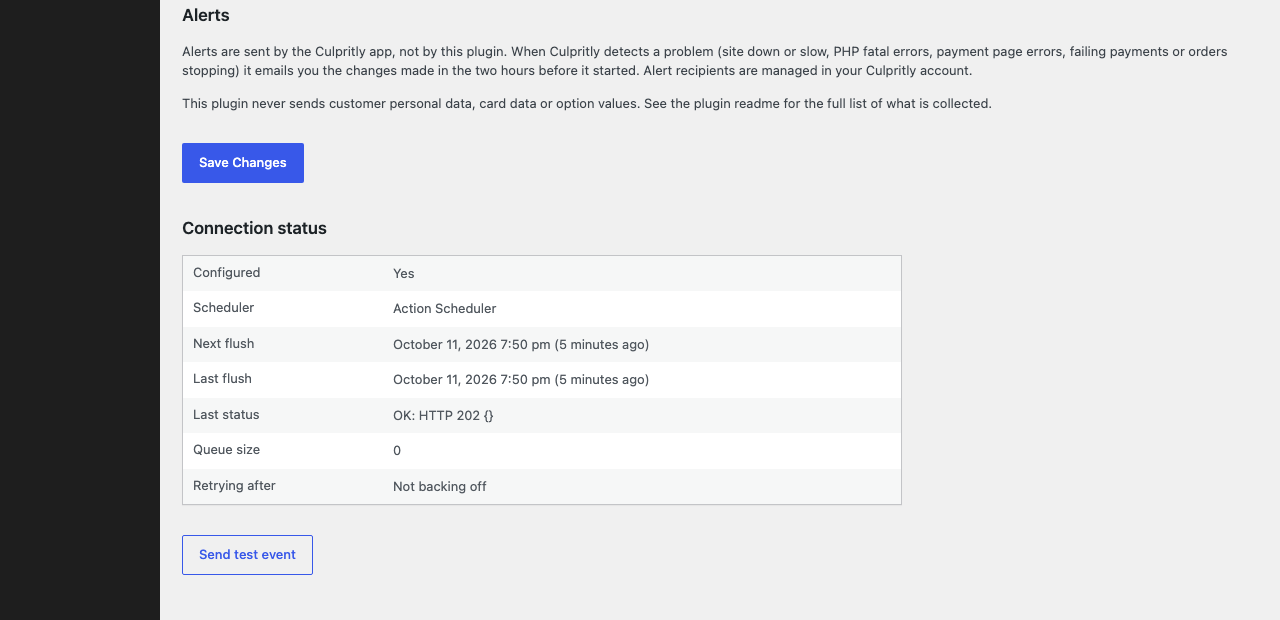
Events are stored in a small local queue and sent to Culpritly every minute with signed requests. If Culpritly is unreachable, events stay in the queue and are retried with backoff.
Culpritly then watches for problems (store down, PHP fatals, failing payments, orders stopping) and emails you the changes made just before the problem started.
What it does not do: it does not send customer personal data, card data or option values, it does not change, block or slow down your checkout, it does not show ads, it adds no front-end credits or links, and it never installs or updates anything.
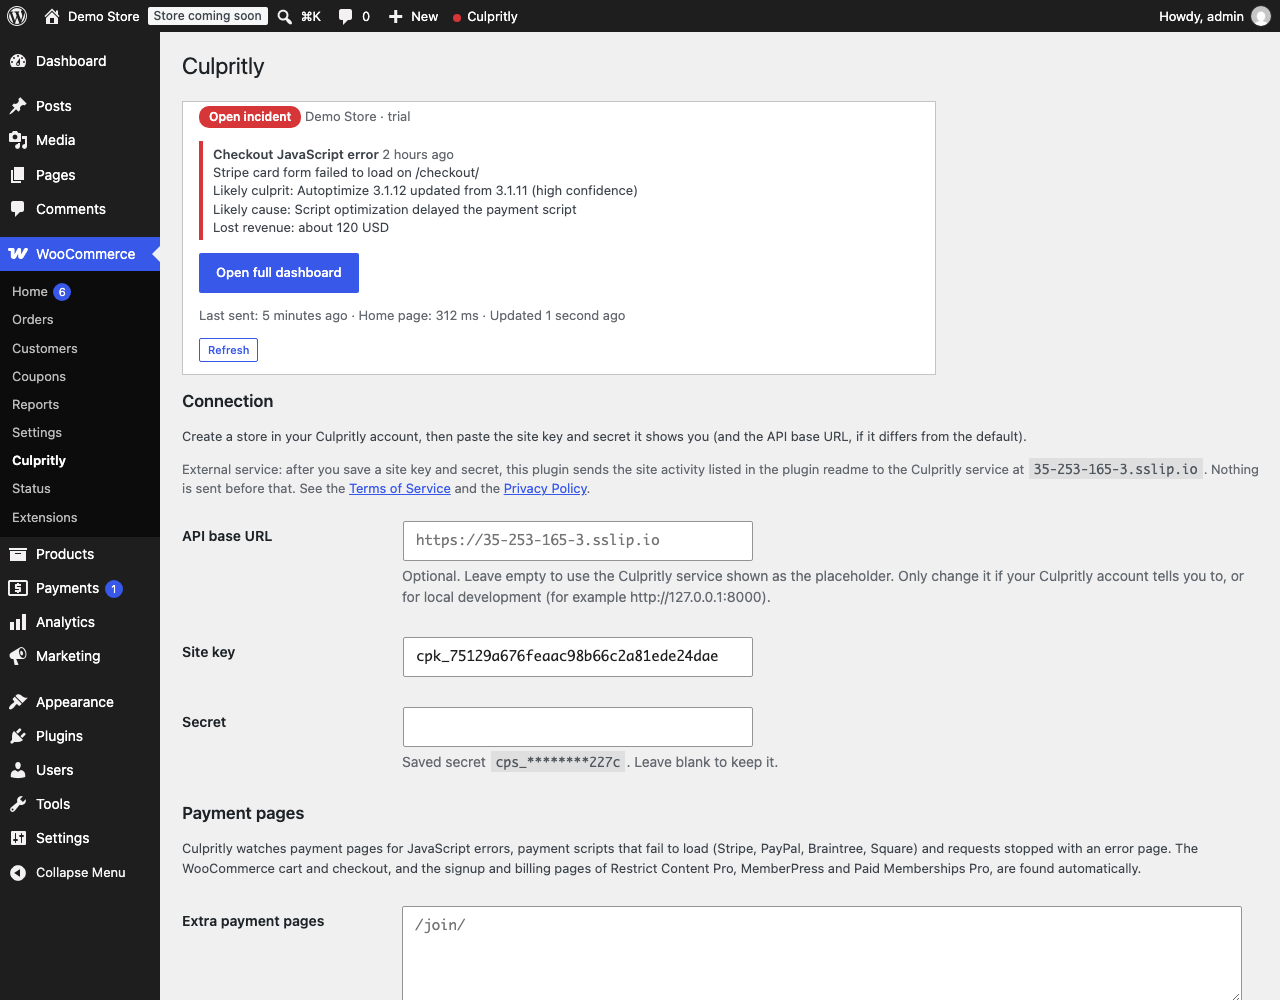
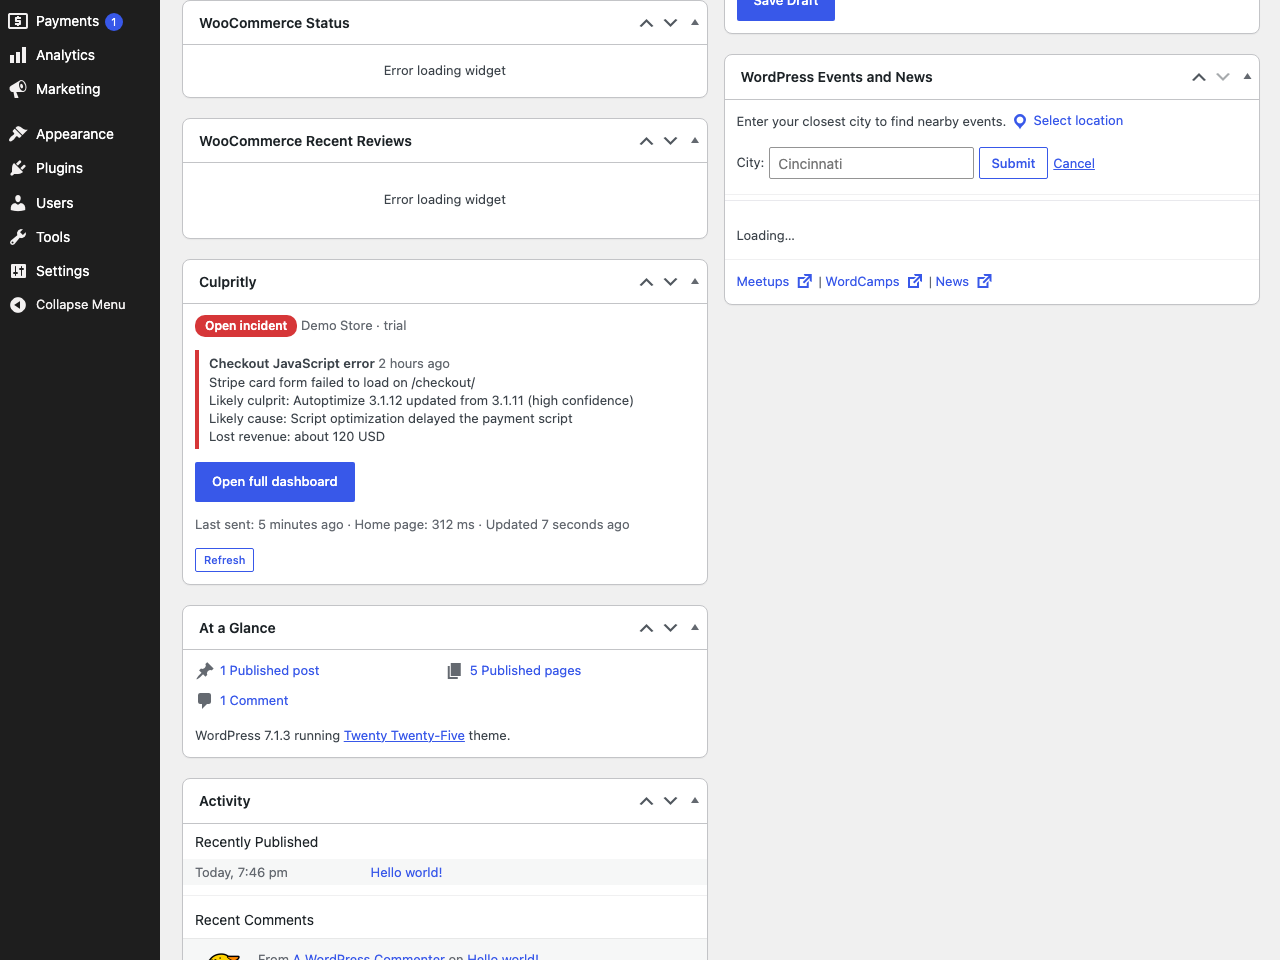
In wp-admin, once connected, the plugin shows the Culpritly status for site administrators: a “Culpritly” dashboard widget (you can hide it in Screen Options) and a panel at the top of its settings page (monitoring state, open incidents with the likely culprit and estimated lost revenue, a link to the full Culpritly dashboard, and when events were last sent), plus a small “Culpritly” item in the admin bar with a coloured dot (green: monitoring, red: open incident, grey: unknown). The status is fetched from Culpritly with a signed request and cached for 5 minutes; the admin bar only reads the cache and never waits on Culpritly. Neither is shown before you connect.
The plugin works without WooCommerce too: change tracking and fatal error capture still run, order signals are simply not recorded.
External services
This plugin connects to the Culpritly service (https://35-253-165-3.sslip.io, the address of the service while its own domain is being set up). Culpritly is operated by Faisal Alvi, the author of this plugin. The service is what turns the data into incident analysis, alerts and a dashboard; the plugin does nothing useful without it.
When the plugin contacts the service. Only after a site owner (an administrator) pastes the site key and secret of a Culpritly store into Culpritly > Settings and saves. That is the opt-in. Before that, nothing is recorded and no request is made. From then on:
- About every minute (WP-Cron or Action Scheduler) queued events are sent to
/api/v1/events. When nothing happened for 10 minutes an empty “heartbeat” batch is sent, so Culpritly can tell a quiet store from a silent connector. - When an administrator opens the dashboard or the Culpritly settings page, or the admin bar needs a refresh (at most every 5 minutes), the plugin requests
/api/v1/statusto show your store status. - When an administrator presses “Send test event”, one test event is sent.
What is sent. Every batch carries your site’s home URL, WordPress, WooCommerce, PHP and plugin versions, currency and timezone. The events are:
- Update, install, activation and theme switch events: plugin, theme and core names, slugs and versions, whether the plugin updates automatically, and the numeric id of the WordPress user who made the change (no name or email).
- Settings changes: the option name, a group, and the names of the changed keys. Never the values.
- PHP fatal errors: error message (up to 1000 characters, absolute paths shortened to paths relative to your WordPress folder), file, line, the plugin or theme it belongs to, and the request path without query string.
- JavaScript errors on payment pages: message (up to 300 characters, email addresses removed), script path without query string, line, column, up to 15 stack frames, and the page type.
- Payment page failures: scripts that failed to load, and the text of wp_die() error pages (tags and email addresses removed).
- Orders: order id, total, currency, payment gateway id and status. For a failed order, the latest private order note as plain text (up to 500 characters, email addresses removed).
- Once after connecting: for each of the last 60 days, the date, the number of paid orders and their total.
- A daily snapshot: WordPress, WooCommerce and PHP versions, installed plugins (name, slug, version, active, automatic updates), the active theme, checkout type (blocks or classic), enabled payment gateway ids, core automatic update level, and notes about active caching, JavaScript optimization, analytics and tag plugins.
What is never sent: customer names, email addresses, postal addresses, phone numbers, IP addresses, order line items or products, payment card data, option values (including API keys), cookies. Error messages and order notes are free text written by other plugins; the plugin strips tags and email addresses and truncates them, but it cannot guarantee that such text never contains something incidental.
Culpritly stores the events to analyse incidents, keeps raw events for 90 days, and may send error messages and the public code or changelog of the plugins involved to an AI provider to explain an incident. The full list of processors is at the subprocessors page linked below.
Payment scripts (Stripe, PayPal, Braintree, Square). The plugin does not contact these companies and sends them nothing. On payment pages it only watches, inside the shopper’s browser, whether the payment scripts your own store already loads (for example Stripe.js or the PayPal SDK) loaded or failed. When one fails, the script’s host name (for example js.stripe.com) and the error type are sent to your own site and then to the Culpritly service above, and nowhere else. Card details and customer data are never read or sent. The host names in the plugin code are only a list used to recognise such scripts.
- Service: https://35-253-165-3.sslip.io
- Terms of Service: https://35-253-165-3.sslip.io/terms
- Privacy Policy: https://35-253-165-3.sslip.io/privacy
- Sub-processors: https://35-253-165-3.sslip.io/subprocessors
The service address is set in one place (CULPRITLY_CONNECTOR_DEFAULT_API_URL in the main plugin file, changeable with the culpritly_connector_default_api_url filter or the optional “API base URL” setting).
Screenshots
Installation
- Install and activate the plugin.
- Create a free account at Culpritly and add a store. Culpritly shows a site key and a secret.
- In WordPress go to WooCommerce > Culpritly (or Settings > Culpritly when WooCommerce is not active).
- Paste the site key and secret, and save. Leave “API base URL” empty unless Culpritly tells you otherwise.
- Click “Send test event” to confirm the connection.
FAQ
-
Does it work without a Culpritly account?
-
No. The plugin only collects and forwards information to the Culpritly service. Without a site key and secret it records nothing and makes no request.
-
What does it cost?
-
The plugin is free. The Culpritly service has a 14 day free trial without a card, then a paid subscription. If your subscription ends, the service stops monitoring; the plugin keeps working, never blocks your store and has no locked features.
-
What data does the plugin send?
-
Only what is listed in the External services section: change events (plugin, theme and core versions, option names with the names of changed keys, edited file paths), PHP fatal error messages with file paths made relative to your WordPress folder, order ids with total, currency, gateway and status, a one-off daily order count and total for the last 60 days, and version information about your site.
-
Does it send customer personal data?
-
No. No customer names, emails, addresses, phone numbers or IP addresses are sent. Order events contain the order id, total, currency, payment gateway and status only. Failed order notes are sent as plain text, truncated to 500 characters, with email addresses removed.
-
Does it send option values, API keys or passwords?
-
No. For settings changes only the option name, a group (WooCommerce, gateway, permalink, cache or other) and the names of the top level keys that changed are sent. Values, including gateway API keys, are never sent.
-
Does it send card data?
-
No. The plugin never reads or sends payment card data.
-
Can I stop it sending data?
-
Yes. Clear the site key on the settings page and save, and the plugin stops recording and sending at once. Deactivating the plugin also stops everything, and deleting it removes its table, options, transients and scheduled jobs.
-
Where is my Culpritly secret stored?
-
In a WordPress option that is not autoloaded. The settings page never shows it in full.
-
What happens if Culpritly is down?
-
Events stay in the local queue (up to 5,000) and are retried with exponential backoff, up to 15 minutes apart. If the queue is full, the oldest order events are dropped first; change events and fatal errors are kept.
-
Does the status widget slow down wp-admin?
-
The dashboard widget and settings panel ask Culpritly for the status at most once every 5 minutes (5 second timeout) and show the last known status, with its age, if Culpritly cannot be reached. The admin bar item only reads the cached status; when it is out of date a background refresh is queued with Action Scheduler or WP-Cron. Only users who can manage options see any of it.
-
Does it add anything to my store front end?
-
Only on payment pages: a small inline script (about 1.5 KB, no external file) that reports JavaScript errors, with the script paths of the error stack (no query strings), to your own site, at most 5 per page view. It sets no cookies and collects no personal data. Visitor IP addresses are only used, hashed, to rate limit reports for a minute and are never stored or sent. Turn it off with the
culpritly_connector_js_listener_enabledfilter.
Reviews
There are no reviews for this plugin.
Contributors & Developers
“Cartsnag Checkout Monitor for Culpritly” is open source software. The following people have contributed to this plugin.
Contributors
Translate “Cartsnag Checkout Monitor for Culpritly” into your language.
Interested in development?
Browse the code, check out the SVN repository, or subscribe to the development log by RSS.
Changelog
0.6.3
- New: when the plugin is not connected yet, the settings page and dashboard widget now show a clear “Start your free 14-day trial” button and the three setup steps. Before, they only said to paste a key.
- New: a single dismissible notice right after activation points to the next step. It shows once, only to administrators, and never once the store is connected.
- New: a “Start free trial” link on the Plugins page until the plugin is connected.
- New: when monitoring is paused or the trial ends soon, the status panel shows a link to the Culpritly billing page.
- Nothing new is recorded or sent. The plugin still contacts the service only after a site key and secret are saved.
0.6.2
- Renamed to Cartsnag Checkout Monitor for Culpritly. New plugin folder, main file and text domain: cartsnag-checkout-monitor-for-culpritly. The plugin author is now Culpritly. Option names, hooks and filters are unchanged.
- The admin stylesheet and the payment page error listener are now enqueued through the WordPress script and style APIs.
- Readme: the External services section now lists the payment SDK host names the plugin recognises and states that it contacts none of them.
0.6.1
- Nothing is recorded, queued or sent until a site key and secret are saved. The dashboard widget and admin bar item only appear once connected (the admin bar item can be turned off with the culpritly_connector_show_admin_bar filter).
- The API base URL is now optional and defaults to the Culpritly service (one constant, filterable).
- The settings page now names the external service and links its Terms of Service and Privacy Policy.
- Uninstall also removes the JavaScript error rate limit transients.
- Readme: External services section.
0.6.0
- The environment snapshot now says which plugins and the active theme update automatically, and the core automatic update level, so Culpritly can show a day-one checkout risk report.
- One-off order history aggregate (orders.history) after you connect: paid orders and total per day for the last 60 days. Dates, counts and totals only. This gives Culpritly a baseline for cost estimates on day one.
- A fresh snapshot is sent once after updating the plugin.
0.5.0
- JavaScript error reports now carry the error stack (up to 15 frames: function, script path without query string, owning plugin or theme, line and column), so incidents can name every script involved, not only the one that threw.
- The environment snapshot now includes the checkout type (blocks or classic), the enabled payment gateways and a note on active JavaScript optimization, caching, analytics and tag plugins.
- PHP fatals on query string routes (wc-api callbacks, wc-ajax, rest_route) now name the handler, so payment webhook failures are recognised.
0.4.0
- “Culpritly” dashboard widget and settings page panel: monitoring state, open incidents with the likely culprit, AI likely cause and estimated lost revenue, link to the full dashboard, last sent time and a refresh button.
- Admin bar item with a status dot, for administrators, using the cached status only.
- Status is read from the new signed GET /api/v1/status and cached for 5 minutes.
0.3.0
- JavaScript error listener now also runs on Restrict Content Pro, MemberPress and Paid Memberships Pro payment pages and on extra payment pages set in the settings.
- Reports payment SDK scripts (Stripe, PayPal, Braintree, Square) that fail to load.
- Records wp_die() error pages on payment page form posts as payment.die events, without changing them.
0.2.0
- Checkout and cart JavaScript error listener with a rate limited REST route, sent as js.error events.
0.1.0
- First release: change recording, PHP fatal capture, order signals, environment snapshot, signed batch sending with backoff, health route and settings page.