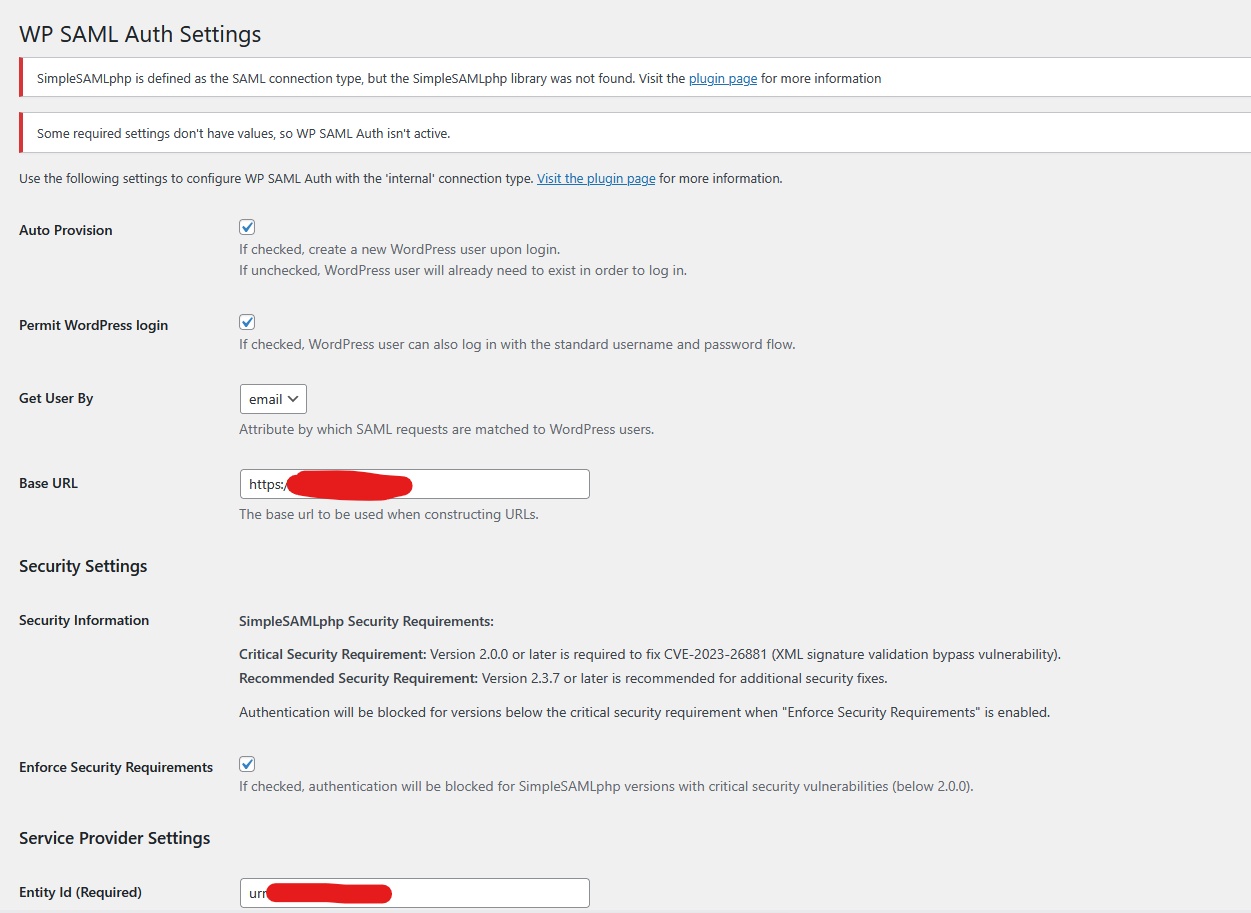
Just installed this plugin for use with Duo at a University. Upon visiting settings I get error “SimpleSAMLphp is defined as the SAML connection type, but the SimpleSAMLphp library was not found”. How do I define the SAML connection type as the bundled OneLogin SAML library instead? I see there’s a filter/function but is there an admin-based settings?
The error you’re seeing suggests the plugin is set to use SimpleSAMLphp as the connection type (which is the default), but the library isn’t installed on your server.
If you’re running version 2.3.0 or later, you should be able to switch the connection type to “Internal (OneLogin)” directly from the plugin’s Settings page in the WordPress admin (Settings > WP SAML Auth). If you’re on an older version, you can set it via a filter; see the README for examples using wp_saml_auth_option.
Regarding metadata, the plugin does not currently generate an SP metadata XML file. You’ll need to provide your IdP with your SP entity ID and ACS URL manually (typically your wp-login.php URL).
Thanks for the quick response! I think I understood that error message, but I am on 2.3.1 and not seeing the ability to select the connection type. Here is the screenshot:
Hi @socialink, thanks for the screenshot. The Settings page is designed to work with the internal (OneLogin) library, there’s no separate connection type selector needed.
The error you’re seeing will clear once all the required fields are filled in and saved. It looks like some required values might still be missing further down the page (IdP SSO URL, x509 Certificate). Once those are saved, the plugin will activate with the OneLogin library automatically.
Could you scroll down and check if all the fields marked as “Required” have values?
The two items under “Identity Provider Settings” (Entity Id and Single SignOn Service URL) are not currently filled in, do you believe that’s the reason? Its a bit of a chicken and an egg since I need to provide those I believe to our IT to get a system going.
The notice is just informational, it goes away once the configuration is complete.
You’re right that it’s a bit of a chicken-and-egg! The SP values your IT team needs are already pre-filled on the Settings page under “Service Provider Settings” (Entity ID and Assertion Consumer Service URL). You can share those with your IT team now, and once they set up the IdP, they’ll give you back the Entity ID and SSO URL to fill in under “Identity Provider Settings.