Title: Diamond Sierra Site Defense
Author: teoleonard
Published: October 30, 2026
Last modified: October 30, 2026
---
Search plugins
# Diamond Sierra Site Defense
By [teoleonard](https://profiles.wordpress.org/teoleonard/)
[Download](https://downloads.wordpress.org/plugin/diamond-sierra-site-defense.1.0.0.zip)
* [Details](https://wordpress.org/plugins/diamond-sierra-site-defense/#description)
* [Reviews](https://wordpress.org/plugins/diamond-sierra-site-defense/#reviews)
* [Installation](https://wordpress.org/plugins/diamond-sierra-site-defense/#installation)
* [Development](https://wordpress.org/plugins/diamond-sierra-site-defense/#developers)
[Support](https://wordpress.org/support/plugin/diamond-sierra-site-defense/)
## Description
Diamond Sierra Site Defense checks your site once a day and tells you – in plain
English – what is wrong and how to fix it. Everything below is free, with no account
to sign up for, and no firewall rules held back for paying users.
**Daily malware scan**
* Compares every WordPress core file against the official checksums from WordPress.
org.
* Compares plugins and themes from the WordPress.org directory against their official
copies, so tampered files (supply-chain attacks) are caught and verified files
are skipped.
* Signature scan of themes, plugins, must-use plugins and uploads for web shells,
obfuscated eval() backdoors, droppers, hidden-admin code and more.
* Detects ClickFix / fake CAPTCHA pages that trick visitors into running commands
on their own computer, clipboard hijacking scripts, and EtherHiding loaders that
pull code from BSC/Polygon smart contracts.
* Detects injected remote `import()` calls in files and on the live homepage.
* Fetches your homepage like a visitor coming from Google, and again as Googlebot,
to catch injections and SEO spam that hide from logged-in users.
* Tracks new and changed PHP files between scans.
* Risky plugin alerts with no setup and no API key: plugins removed from WordPress.
org for a security issue, security updates waiting (found in the plugin’s changelog)
and plugins abandoned for over two years.
* Optional: checks whether Google Safe Browsing is warning visitors away from the
site (off until you turn it on).
* Runs in small steps, so it works on shared hosting without timeouts.
**Fixes**
* Restore a modified core, plugin or theme file with the verified original from
WordPress.org.
* Quarantine suspicious files – restorable from the Quarantine tab.
* A verification scan runs automatically after a fix to confirm the malware is
really gone.
**Firewall**
* Blocks SQL injection, XSS, path traversal, remote file inclusion, command injection
and PHP object injection.
* Blocks executable and disguised PHP uploads and SVGs with embedded scripts.
* Blocks vulnerability scanners and probes for .env, .git, wp-config backups and
known shell names.
* Inspects JSON sent to the REST API and cookies, not just forms.
* Repeat offenders are blocked automatically.
* Log-only mode: see what would be blocked before anything is. New installs log
for their first week, then start blocking on their own.
**Login protection**
* Two-factor login with any authenticator app (Google Authenticator, Microsoft
Authenticator, 1Password, Authy…), with one-time backup codes.
* CAPTCHA on the login, registration, lost-password and comment forms: a built-
in math question (no account needed), Cloudflare Turnstile, Google reCAPTCHA
v2 or hCaptcha – with step-by-step instructions for getting the keys. A CAPTCHA
outage or a wrong key never locks you out.
* Refuses passwords found in known data breaches (Have I Been Pwned, k-anonymity–
the password never leaves your site).
* Custom login URL – move the login page off wp-login.php so bots can’t find it.
* Login form honeypot that blocks automated login bots with nothing for real visitors
to solve.
* Limits failed logins per IP and per account, with escalating lockouts. IPs an
account has used before are never locked out, so nobody can lock you out of your
own site.
* Trap usernames (like “admin”) get bots locked out on the first try.
* Generic error messages that don’t reveal whether a username exists.
**Email alerts**
* Scan found a serious problem (and, if you like, an all-clear after every scan).
* An administrator signed in from a new IP.
* A new administrator account was created, or someone was promoted to administrator.
* Diamond Sierra Site Defense itself was deactivated – malware often switches security
plugins off first.
* Plugin, theme and WordPress updates are waiting (only when a new one appears).
* An IP or an account was locked out after failed logins (optional, at most once
an hour).
**Hardening**
* Disable XML-RPC, the file editor, application passwords and username enumeration.
* Block PHP execution in uploads, sensitive files and directory listing.
* Security headers and hidden version numbers.
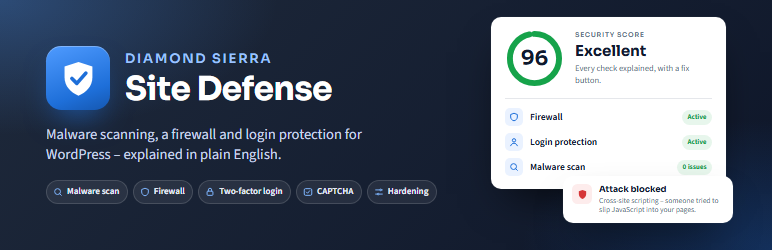
* A security score that explains every check, each with its own Apply button.
**Also**
* Works alongside Wordfence, All-In-One Security, Solid Security, Sucuri, MalCare,
Defender, Shield, Loginizer and others: Site Defense pauses its own firewall
and login limits so the same visitor isn’t blocked twice, and keeps scanning.
* Multisite: network-activate it to protect every site. The scanner and settings
are for super admins only.
* Results in Tools Site Health, and WP-CLI commands to get back in after a lockout(`
wp site-defense unblock`, `reset-login-url`, `2fa-reset`).
**Diamond Sierra Site Defense Pro**
An optional add-on for people who clean hacked sites or look after many: one-click
database cleanup, “Fix automatically”, the post-hack recovery kit, protection against
stolen login cookies, supply-chain and WooCommerce checkout watches, CVE matching,
an alert centre with Slack/Discord, an activity log and white-labelling. Everything
listed above stays free. Details at [diamondsierra.com](https://diamondsierra.com/diamond-sierra-site-defense-pro/)
### External services
Diamond Sierra Site Defense connects to these services. Apart from the WordPress.
org checks, each one is off until you turn it on.
* **WordPress.org** (api.wordpress.org, downloads.wordpress.org, core.svn.wordpress.
org, plugins.svn.wordpress.org, themes.svn.wordpress.org) – to download official
checksums, theme packages and clean copies of files when you restore or repair
them, and to read the public directory entry of each installed plugin (whether
it was closed, when it was last updated, and the changelog of a waiting update).
Only the names and versions of WordPress, your plugins and your themes are sent–
the same information WordPress itself sends when it checks for updates. [Terms](https://wordpress.org/about/privacy/)
* **Have I Been Pwned – Pwned Passwords** (api.pwnedpasswords.com) – only if you
turn on “Block breached passwords”. When a password is set, and once a day at
login, the first 5 characters of the password’s SHA-1 hash are sent; the password
itself and the rest of the hash never leave your site. [Terms and privacy](https://haveibeenpwned.com/Privacy)
* **Cloudflare Turnstile** (challenges.cloudflare.com) – only if you choose Turnstile
as the CAPTCHA. Its script is loaded on the protected forms, and on submit the
visitor’s token and IP address are sent to Cloudflare to check them. [Terms](https://www.cloudflare.com/website-terms/)·
[Privacy](https://www.cloudflare.com/privacypolicy/)
* **Google reCAPTCHA** (www.google.com/recaptcha) – only if you choose reCAPTCHA
as the CAPTCHA. Its script is loaded on the protected forms, and on submit the
visitor’s token and IP address are sent to Google to check them. [Terms](https://policies.google.com/terms)·
[Privacy](https://policies.google.com/privacy)
* **hCaptcha** (js.hcaptcha.com, api.hcaptcha.com) – only if you choose hCaptcha
as the CAPTCHA. Its script is loaded on the protected forms, and on submit the
visitor’s token and IP address are sent to hCaptcha to check them. [Terms](https://www.hcaptcha.com/terms)·
[Privacy](https://www.hcaptcha.com/privacy)
* **Google Safe Browsing** – only if you turn on the blocklist check under Settings
Malware scanner. Once per scan, your site’s address is sent to Google to find
out whether it is blocklisted. With an API key the request goes to safebrowsing.
googleapis.com; without a key, and only if you also tick “Check without a key”,
it goes to transparencyreport.google.com. Nothing else is sent. [Terms](https://policies.google.com/terms)·
[Privacy](https://policies.google.com/privacy)
### Privacy
* Everything Site Defense records stays in your own database. Nothing is sent to
us. The only outside connections are the ones listed under External services.
* The firewall and login logs store the visitor’s IP address, the address they
requested and their browser’s user agent, so you can see who was blocked and
why. Log lines are deleted after 30 days, and the log never grows past 20,000
lines.
* Blocked IPs are kept until their block ends.
* For each user it keeps the last 10 IP addresses they logged in from (so nobody
is locked out of their own account and new-IP alerts work), and, if they turn
on two-factor login, the authenticator secret and hashed backup codes.
* The plugin sets no cookies of its own.
* Only administrators (super admins on multisite) can see the logs and settings.
* Deleting the plugin removes its tables, settings, user data and quarantined files.
## Screenshots
[⌊Dashboard: security score, open issues and one-click updates.⌉⌊Dashboard: security
score, open issues and one-click updates.⌉[
Dashboard: security score, open issues and one-click updates.
[⌊Scan results with one-click fixes – restore the original file from WordPress.org,
or quarantine it.⌉⌊Scan results with one-click fixes – restore the original file
from WordPress.org, or quarantine it.⌉[
Scan results with one-click fixes – restore the original file from WordPress.org,
or quarantine it.
[⌊Two-factor login on the user profile.⌉⌊Two-factor login on the user profile.⌉[
Two-factor login on the user profile.
[⌊Hardening: every protection explained, each with its own Apply button.⌉⌊Hardening:
every protection explained, each with its own Apply button.⌉[
Hardening: every protection explained, each with its own Apply button.
[⌊Firewall: blocked IPs and the log.⌉⌊Firewall: blocked IPs and the log.⌉[
Firewall: blocked IPs and the log.
[⌊Settings.⌉⌊Settings.⌉[
Settings.
## Installation
1. Upload the plugin folder to `/wp-content/plugins/` or install the zip from Plugins
Add New.
2. Activate it.
3. Go to **Site Defense Dashboard** and click **Scan now** to build the first baseline.
4. If your site is behind Cloudflare, set **Settings Visitor IP comes from** to Cloudflare.
The daily scan uses WP-Cron. On low-traffic sites, a real cron job calling `wp-cron.
php` every 5 minutes makes sure it always runs on time.
## FAQ
### Do I need a Google API key for the blocklist check?
The blocklist check is off by default. To use it, turn on **Settings Malware scanner
Google blocklist check** and either paste a free Safe Browsing API key from Google
Cloud (recommended, it’s Google’s official API) or tick **Check without a key**
to read the public status from Google’s Transparency Report instead.
### My site is behind a load balancer. Which IP setting do I use?
Pick **X-Forwarded-For**. Site Defense reads that header from the right and takes
the first public address, so a visitor can’t fake their IP by sending the header
themselves. Behind Cloudflare, pick **Cloudflare** instead.
### I use nginx – is the uploads protection active?
nginx ignores .htaccess files. Add this to your server block:
```
location ~* /wp-content/uploads/.*\.php$ { deny all; }
```
### A finding is a false positive. What do I do?
Click **Ignore**. It stays hidden until that file or content changes.
### Can I use it with Wordfence or All-In-One Security?
Yes. Run only one firewall – by default Site Defense steps aside and lets the other
plugin handle the firewall and login limits, while it keeps scanning and cleaning.
If you’d rather use Site Defense’s firewall, switch the other plugin’s firewall
off and untick “Step aside for other security plugins” in Settings.
### I use Jetpack / the mobile app
Untick **Disable XML-RPC** in Settings.
### I locked myself out by the firewall
With WP-CLI: `wp site-defense unblock `. Without it, add `define( 'DSSD_DISABLE_FIREWALL',
true );` to wp-config.php, log in, add your IP under **Settings Never block these
IPs**, then remove the line again.
### I lost my phone and can’t get past two-factor login
Type one of your backup codes instead of the 6-digit code. No backup codes? Ask
another administrator to click **Turn off** under Two-factor login on your user
profile, run `wp site-defense 2fa-reset `, or add `define( 'DSSD_DISABLE_2FA',
true );` to wp-config.php, log in, set it up again, then remove the line.
### Why does the firewall say “Would block (log only)”?
New installs spend their first week in log-only mode so you can spot false alarms–
a contact form or plugin that legitimately sends code-like text. Check the Firewall
tab, then click **Start blocking now**, or wait and it starts on its own.
### I set a custom login URL and can’t find it
Add `define( 'DSSD_DISABLE_LOGIN_URL', true );` to wp-config.php. wp-login.php works
normally again straight away. Log in, check or clear the URL under **Settings Login
protection**, then remove the line.
### Does the custom login URL work on multisite?
No. On a network, renaming the login page would break sign-on across sites, so the
feature turns itself off there automatically.
### Does Site Defense work on multisite?
Yes – network-activate it. The firewall, login protection, two-factor login, Turnstile
and the activity log protect every site. The scanner, cleanup tools and settings
live in the main site’s dashboard and are for super admins only, because they work
on files shared by the whole network. Settings apply to all sites.
### Can I extend it?
Yes. Filters and actions include `dssd_signatures`, `dssd_firewall_rules`, `dssd_scan_recurrence`,`
dssd_settings_defaults`, `dssd_settings_sanitize`, `dssd_settings_cards`, `dssd_admin_tabs`,`
dssd_render_tab_{tab}`, `dssd_brand_name`, `dssd_menu_label`, `dssd_show_branding`,`
dssd_import_allowlist`, `dssd_allow_xmlrpc` and `dssd_loaded`.
## Reviews
There are no reviews for this plugin.
## Contributors & Developers
“Diamond Sierra Site Defense” is open source software. The following people have
contributed to this plugin.
Contributors
* [ teoleonard ](https://profiles.wordpress.org/teoleonard/)
[Translate “Diamond Sierra Site Defense” into your language.](https://translate.wordpress.org/projects/wp-plugins/diamond-sierra-site-defense)
### Interested in development?
[Browse the code](https://plugins.trac.wordpress.org/browser/diamond-sierra-site-defense/),
check out the [SVN repository](https://plugins.svn.wordpress.org/diamond-sierra-site-defense/),
or subscribe to the [development log](https://plugins.trac.wordpress.org/log/diamond-sierra-site-defense/)
by [RSS](https://plugins.trac.wordpress.org/log/diamond-sierra-site-defense/?limit=100&mode=stop_on_copy&format=rss).
## Changelog
#### 1.0.0
* First release.
## Meta
* Version **1.0.0**
* Last updated **1 day ago**
* Active installations **Fewer than 10**
* WordPress version ** 5.8 or higher **
* Tested up to **7.1.4**
* PHP version ** 7.4 or higher **
* Tags
* [firewall](https://wordpress.org/plugins/tags/firewall/)[login protection](https://wordpress.org/plugins/tags/login-protection/)
[malware scanner](https://wordpress.org/plugins/tags/malware-scanner/)[security](https://wordpress.org/plugins/tags/security/)
* [Advanced View](https://wordpress.org/plugins/diamond-sierra-site-defense/advanced/)
## Ratings
No reviews have been submitted yet.
[Your review](https://wordpress.org/support/plugin/diamond-sierra-site-defense/reviews/#new-post)
[See all reviews](https://wordpress.org/support/plugin/diamond-sierra-site-defense/reviews/)
## Contributors
* [ teoleonard ](https://profiles.wordpress.org/teoleonard/)
## Support
Got something to say? Need help?
[View support forum](https://wordpress.org/support/plugin/diamond-sierra-site-defense/)